Local-first governed MCP memory backend for coding agents.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
One-click editor setup isn’t available for this listing yet — we don’t have a confirmed install command, and we’d rather show nothing than point your editor at the wrong package or host. Follow the project’s own setup instructions, linked above.
Manual Client & Custom JSON ConfigExpand JSON ▾
No confirmed setup config for this listing yet. We only publish a config block when the install details come from the project itself — its README, its docs, or a verified owner. We haven’t found those for MemoryGuard, and we’d rather show nothing than a guess you’d paste into your client. Follow the project’s own setup instructions for the current steps.
Documentation Overview
MemoryGuard
Governed shared memory for coding agents.
Local-first MCP memory with automatic organization, scoped rules, evidence, and rollback.



Let agents write without turning shared memory into an unreviewed pile. MemoryGuard organizes each write, preserves the evidence behind changes, and keeps governance decisions reversible.
No account. No remote server. No remote telemetry. Local-only usage telemetry is optional and stores bounded, privacy-preserving aggregates locally.
Quick start · Upgrade · Knowledge Library · Architecture · Supported hosts · Privacy and safety
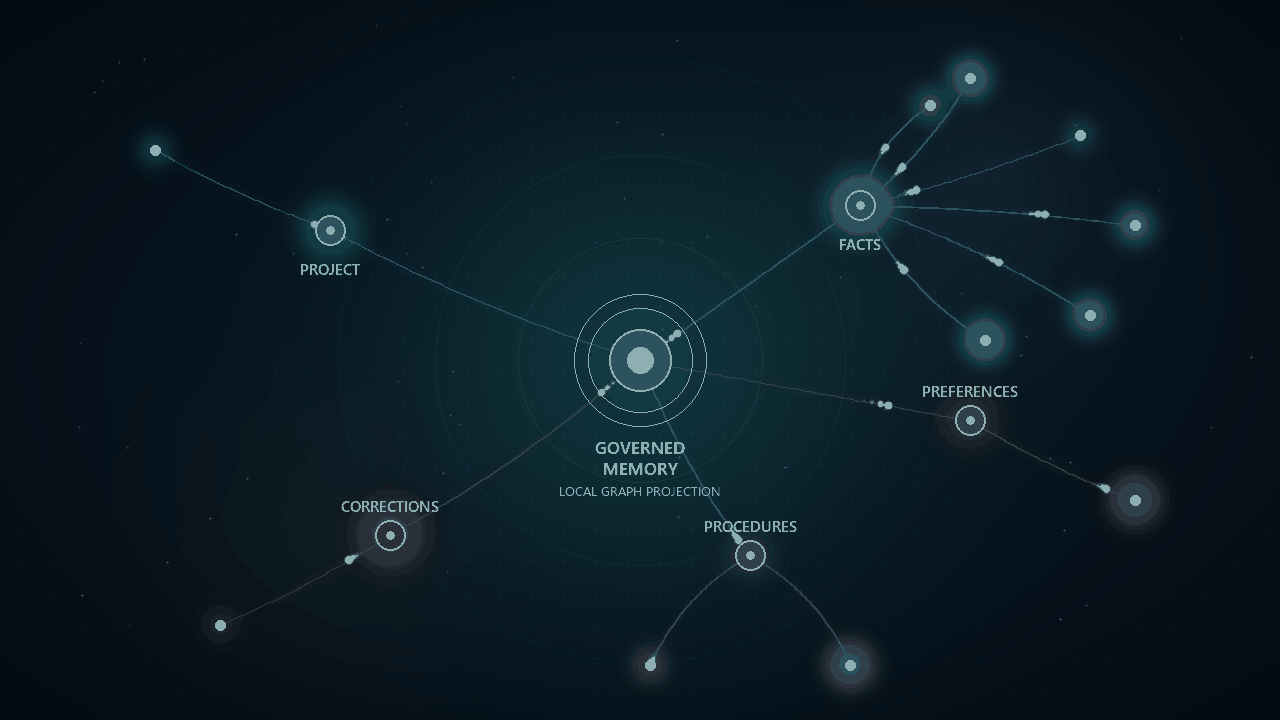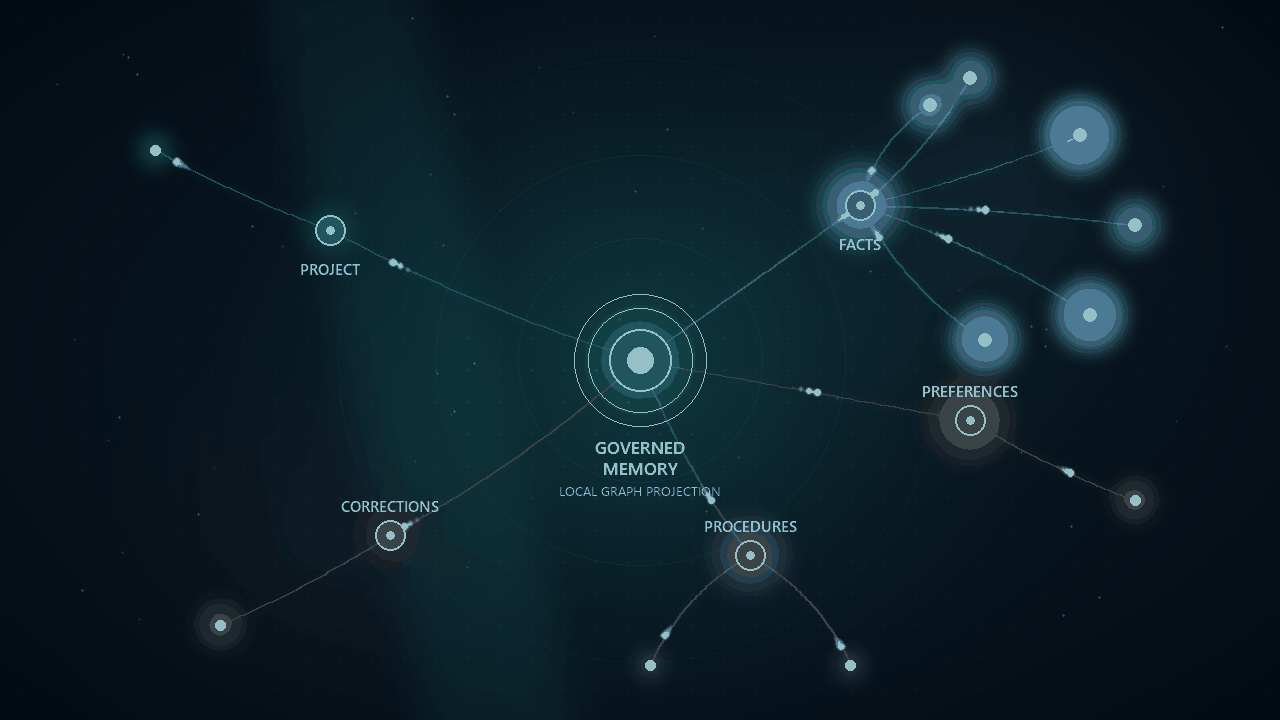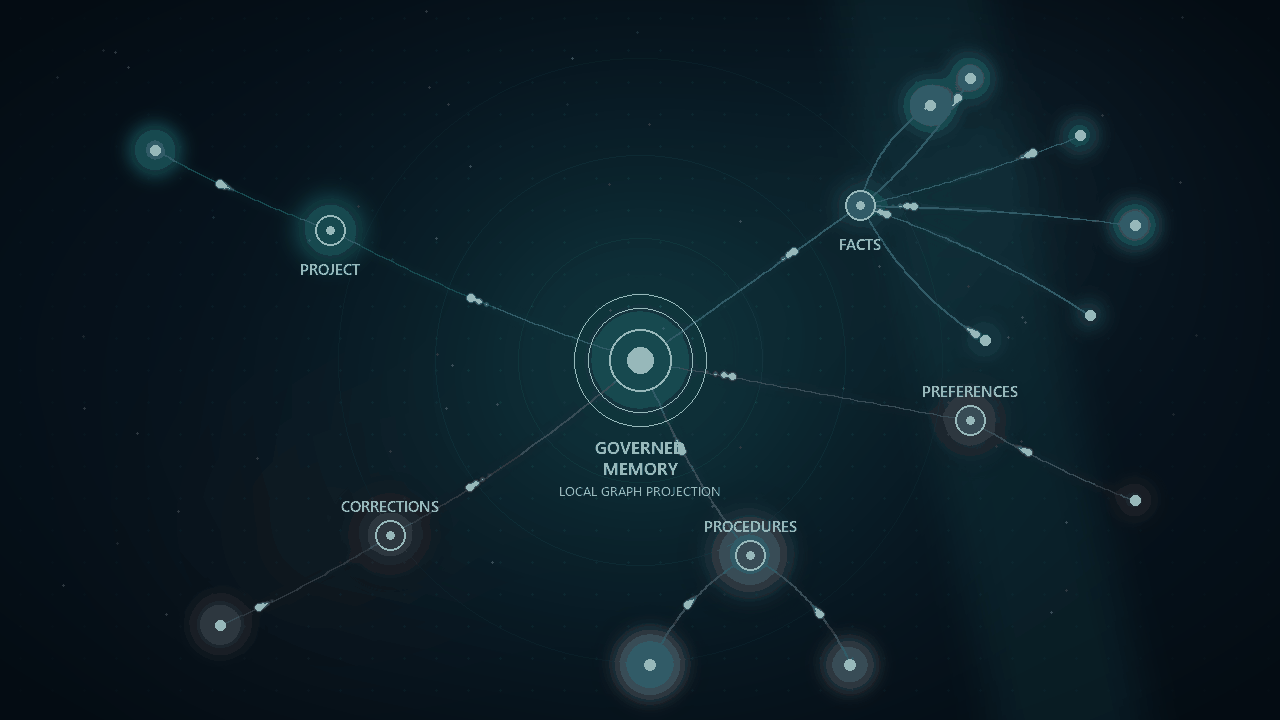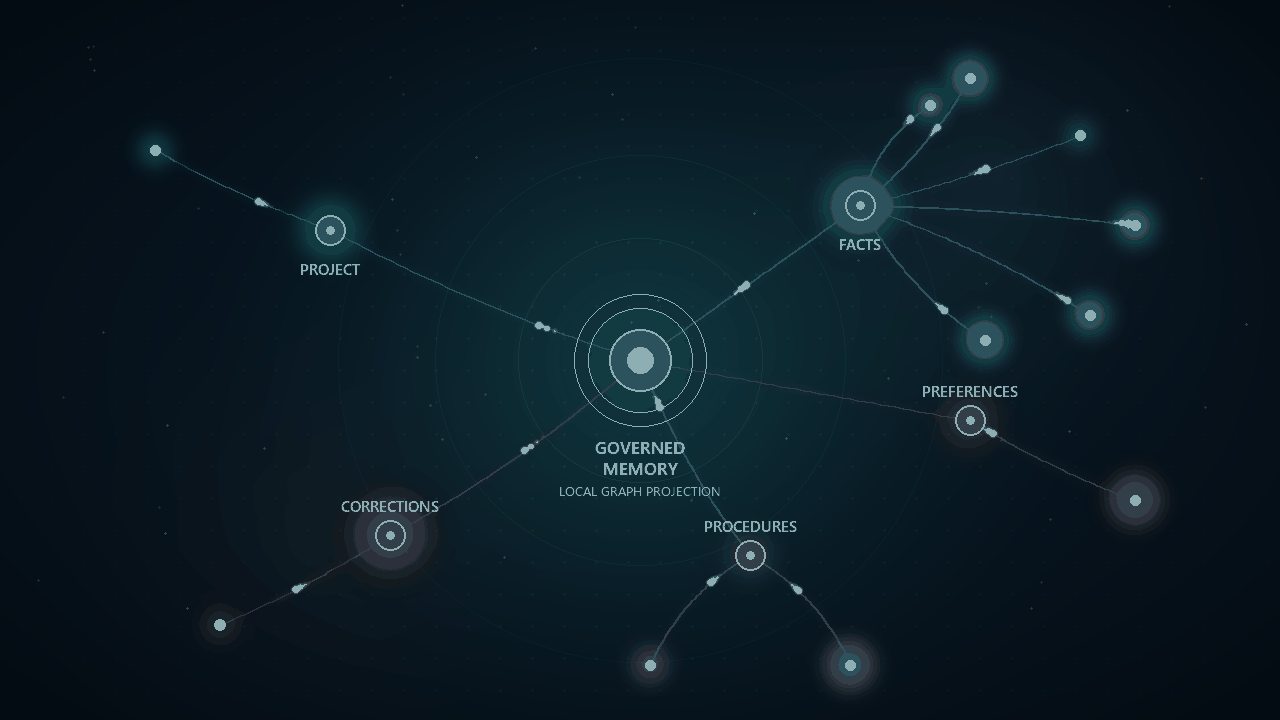
A synthetic governed projection: signals move through memory categories while raw conversation text remains outside the graph.
What's New in v0.7.13
v0.7.13 strengthens mandatory-rule replacement and recovery, improves audience-aware identity handling, and improves conflict resolution:
- Safe mandatory-rule replacement: Replacements validate the final mandatory package against audience matching, canonical rules, deduplication, sensitivity checks, and publication budgets. Equivalent unlocked predecessors retire in the same transaction; failed validation rolls back the complete update. See the replacement and recovery details.
- Native Agent/group audience matching: Matching and deduplication no longer split the same native audience solely by provider or runtime role. Distinct Agent identities remain separate, and project-scoped audiences retain their project boundaries. Provider repair uses the verified identity for its target provider.
- Readable, atomic conflict resolution: Conflict views preserve readable peer information, and resolution keeps peer groups intact while applying the selected changes atomically. Ambiguous conflicts remain unresolved.
- Cursor Hook protection: Cursor MemoryGuard Hooks now use a 30-second
timeout, up from 15 seconds, with
failClosed: true.
v0.7.14 only corrects release metadata for the GitHub repository rename; it does not change runtime behavior. See the v0.7.14 release note.
See the v0.7.13 release note and release history.
Earlier release details are kept in the Changelog and GitHub release records.
Token evidence and demo
Usage events distinguish measured_cached_input from
measured_cache_write_input. measured_cache_coverage.cache_read and
cache_write report complete, partial, or unavailable; measured zero
remains 0, while missing provider data remains None/unavailable.
Character-based estimates remain explicitly labelled
estimated mg_deterministic_unit, never provider tokens.
Run the benchmark only against an authorized local workspace:
Read the benchmark guide for measured, estimated, derived, and unsupported semantics. Use the demo recording checklist for a sanitized walkthrough. The repository's synthetic graph artwork is not a live product capture; it is not evidence of usage or savings.
Major V2 refactor in v0.6.0
v0.6.0 was a production data-plane refactor, not a storage-only upgrade:
- Authoritative V2 domains: Memory, Rules, Evidence, Content, Runtime, Projection, Assets, CodeGraph, Skills, and System state are separated into explicit SQLite domains with governed boundaries.
- Explicit cutover:
V1_ACTIVE → V2_BUILDING → V2_READY → V2_ACTIVEis fail-closed; V2 never silently falls back to legacy stores or dual-writes after READY/ACTIVE. - Lossless migration: frozen-source preparation uses coherent SQLite online backups, validates source/target evidence, rechecks live-source drift, and preserves V1 data plus migration backups for rollback.
- Native routing: MCP, CLI, GUI, and Hook surfaces are classified explicitly; the release closed the 233-surface cutover with 138 implemented routes, 95 retired routes, and zero neutral/blocker routes.
- Governed intelligence: Rule lifecycle and RuleMerge, extraction/enrichment, External MCP import, provider control-plane, conversation history, Knowledge Library, and GUI governance all use the V2 evidence and decision paths.
- Operational evidence: Reference Audit, per-domain SQLite health, guarded maintenance, rollback evidence, and safe unbound diagnostics are part of readiness and operations.
Why MemoryGuard
Persistent memory solves storage. It does not solve governance.
When several coding agents write into the same context, records become duplicated, stale, contradictory, over-broad, or unsafe to reuse. MemoryGuard sits between coding agents and their shared memory to keep that context usable.
| Without governance | With MemoryGuard |
|---|---|
| Notes accumulate without a canonical state | Writes are classified, deduplicated, superseded, or surfaced as conflicts |
| A correction silently destroys the old value | Evidence and supersede chains preserve what changed and why |
| Tokens and credentials can remain active | Sensitive-looking content is quarantined from active memory |
| Every write needs manual approval | Agents write normally; people review exceptions and outcomes |
| Raw chat logs leak into future context | Conversation history remains a separate, explicitly read evidence archive |
System architecture
Related MCP Servers
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about MemoryGuard
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/memoryguard-2)HTML Embed
<a href="https://allmcps.com/mcp/memoryguard-2"><img src="https://allmcps.com/api/badge/memoryguard-2?style=directory" alt="MemoryGuard on AllMCPs" /></a>