
Security tools for your AI: scan, pentest, check headers, guard code and scan repos for secrets.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
One-click editor setup isn’t available for this listing yet — we don’t have a confirmed install command, and we’d rather show nothing than point your editor at the wrong package or host. Follow the project’s own setup instructions, linked above.
Manual Client & Custom JSON ConfigExpand JSON ▾
No confirmed setup config for this listing yet. We only publish a config block when the install details come from the project itself — its README, its docs, or a verified owner. We haven’t found those for unesLam/jikida, and we’d rather show nothing than a guess you’d paste into your client. Follow the project’s own setup instructions for the current steps.
Documentation Overview
Jikida.io
The hosted AI pentester for people who ship — not just security engineers.
Pentest your live app, scan your repo, protect it with a WAF, and watch its uptime. One account. No Docker, no LLM key, free tier.



Why it beats Nuclei / Strix / Shannon ↓ · Install · MCP · SDKs · Compare
Install it, scan it, or plug it into your AI editor:
Pentest & scan for developers, AI IDEs & vibe coders
Pentest and scan websites, web apps, code and GitHub for vulnerabilities and exposed keys. Secure vibe-coded apps, monitor uptime, SSL and domains, and rate-limit APIs. One platform.
Website & app pentest · Code & repo scan · Deep pentest · MCP for AI IDEs · Agentic & vibe-coded security · SDKs
Jikida.io is a developer-first security platform. The core is pentest and scanning: it pentests your live website and app, scans your code and connected GitHub/GitLab/Bitbucket repos for exposed secrets and vulnerable dependencies, runs a deeper authenticated pentest, and plugs into your AI IDE (Claude Code, Cursor, Windsurf) over MCP so it guides agentic and vibe-coded work to write secure code and catches mistakes before they ship. Uptime, SSL & domain monitoring, a managed WAF, and a compliance generator come bundled as complementary extras — installed in one line for Node, PHP/Laravel, Python, Go, Ruby, Java, .NET, Rust, Bun, or Deno.
Your security layer. Shipped in 30 seconds. One line — npx @jikida/init — and every SDK fails open, so if Jikida.io is ever down your app keeps serving.
Why Jikida beats the other security tools
The strongest open-source security tools are deep but narrow — pentest-only, self-hosted, bring-your-own-LLM-key. Jikida does the deep work and hosts it, runs with no key of your own, and adds a WAF, uptime and repo scan the pentest-only tools skip. ✅ full · ⚠️ partial · ❌ none.
| Jikida | Nuclei | Strix | Shannon | Snyk | Cloudflare | |
|---|---|---|---|---|---|---|
| Live-app pentest with real exploit | ✅ | ⚠️ match | ✅ | ✅ | ❌ | ❌ |
| SAST + DAST (code and live app) | ✅ | ⚠️ DAST | ✅ | ✅ | ⚠️ SAST | ❌ |
| Repo secret + CVE (OSV) scan | ✅ | ❌ | ⚠️ | ⚠️ | ✅ | ❌ |
| Managed WAF (blocks live attacks) | ✅ | ❌ | ❌ | ❌ | ❌ | ✅ |
| Uptime + SSL / domain monitoring | ✅ | ❌ | ❌ | ❌ | ❌ | ⚠️ |
| Hosted — no Docker, no self-host | ✅ | ⚠️ cloud | ❌ | ❌ | ✅ | ✅ |
| Runs with no LLM key of yours | ✅ | ✅ | ❌ BYOK | ❌ BYOK | ✅ | ✅ |
Install: CLI + Docker + npx | ✅ all | ⚠️ CLI | ⚠️ Docker | ⚠️ npx | ⚠️ CLI | ⚠️ DNS |
| MCP tools in your AI editor | ✅ | ❌ | ❌ | ⚠️ | ❌ | ❌ |
| Free tier, no card | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
The one axis the AI pentesters still go deeper on is raw exploitation — exactly what our source-to-exploit deep pentest is closing. Everywhere else, the builder who shipped with Cursor last week wins with Jikida: nothing to self-host, no key to buy, the whole stack in one account. Full breakdowns: nuclei · strix · shannon · snyk · cloudflare.
Get started — pick your entry point
Every command below sits in its own copy box. Lines that start with ! are notes, not commands — do not copy those.
Scan a URL or repo — no account needed.
! Scan a local repo for committed secrets:
Add the WAF + SDK — auto-detects your framework.
Install a language SDK — Node shown; PHP, Python, Go and the rest are in the SDK table.
MCP server for Claude Code, Cursor and Windsurf — add this to ~/.claude/mcp.json:
Agent skills — copy the skills/ folder into your assistant's skills folder (.claude/skills/, Cursor rules, and the like). Three skills: security, clean-code, UX design — see the table below.
Full details for each are below.
Where things live
| Folder | What it holds |
|---|---|
sdks/ | Ten language SDKs — Node, PHP, Python, Go, Ruby, Java, .NET, Rust, Bun, Deno. |
tools/ | The scan CLI, the init onboarding CLI, and the mcp server. |
skills/ | The Jikida agent skill for Claude Code, Cursor and Windsurf. |
waf-rules/ | Versioned WAF rule packs (OWASP Top 10, API abuse, bot scanners, vibe-coder). |
Get a token at app.jikida.io/developer. Set it as JIKIDA_TOKEN.
See it in action
One dashboard for a site's whole security posture — protection status, uptime, pentest grade, email security (SPF/DKIM/DMARC) and compliance — with instant alerts to your phone, Slack, Telegram, Discord, email or a webhook.
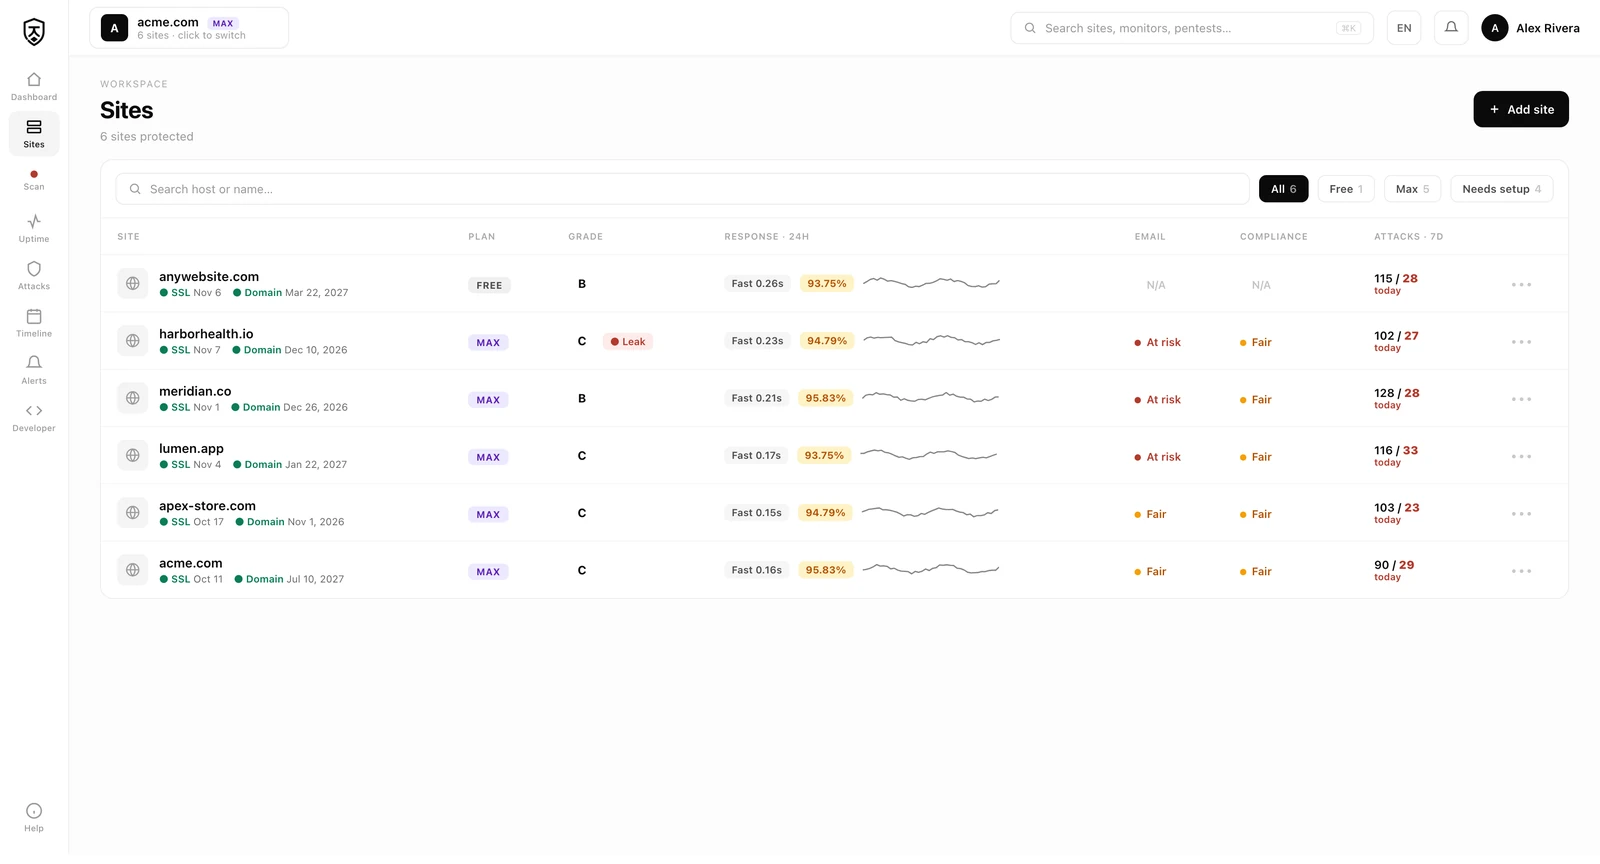
- Uptime & performance — response-time trend, uptime %, P95 and an incident timeline for every page and API you watch.
- API rate-limits & rules — your SDK auto-detects endpoints from real traffic; approve per-endpoint rate caps and WAF rules, or dismiss the ones you don't need.
Table of contents
- Why Jikida beats the other security tools
- Why Jikida.io
- How access works
- What's inside
- Quick install
- Security for your stack
- SDKs — every language
- MCP server for AI IDEs
- Free tools
- Skill for Claude Code
- Standards & mappings
- Threats Jikida.io stops
- Contributing
Why Jikida.io
Most small teams ship without a Web Application Firewall in front of their app. They know they should. They put it on the backlog. Then the free trial ends, or a user reports a slow page, and the WAF ticket rots another quarter.
Jikida.io removes three specific frictions:
- Install — one line, one language, five minutes.
- Downside risk — every SDK is fail-open. If Jikida.io is down, your app keeps serving. You lose protection, not availability.
- Cost — there's a real free tier that protects a hobby project. Plans and current pricing live at jikida.io.
How access works — free, then account-gated, then plan-gated
Everything in this repo is open source, and a lot of Jikida.io is usable before you ever sign up. The model is three tiers of friction, on purpose:
Related MCP Servers
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about Jikida
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/uneslam-jikida)HTML Embed
<a href="https://allmcps.com/mcp/uneslam-jikida"><img src="https://allmcps.com/api/badge/uneslam-jikida?style=directory" alt="Jikida on AllMCPs" /></a>