Evidence-first security review of authorized repositories. Read-only, root-confined, no shell.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
One-click editor setup isn’t available for this listing yet — we don’t have a confirmed install command, and we’d rather show nothing than point your editor at the wrong package or host. Follow the project’s own setup instructions, linked above.
Manual Client & Custom JSON ConfigExpand JSON ▾
No confirmed setup config for this listing yet. We only publish a config block when the install details come from the project itself — its README, its docs, or a verified owner. We haven’t found those for SecHelix, and we’d rather show nothing than a guess you’d paste into your client. Follow the project’s own setup instructions for the current steps.
Documentation Overview
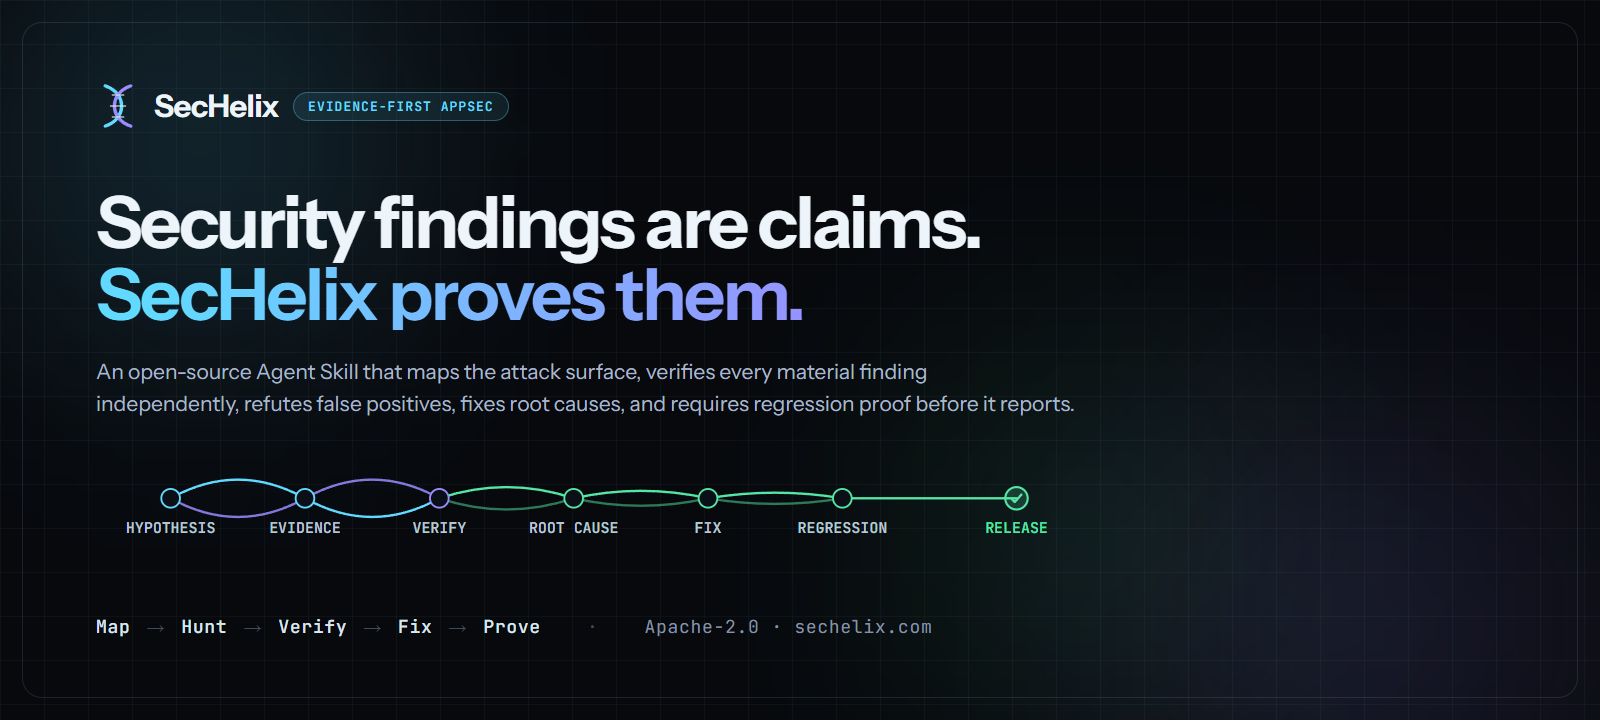
Most AI security tools try to find more. SecHelix tries to prove itself wrong.
SecHelix
Every candidate finding goes to an independent verifier whose only job is to disprove it. The
report shows you what it refuted and why — and returns INCOMPLETE rather than a clean PASS when
it could not actually check.
Open source, Apache-2.0, for code you own or are authorized to test. Runs in Claude Code, Codex, Copilot and other Agent Skills-compatible agents; the Python runtime is optional.
It helps a coding agent:
- map the attack surface and trust boundaries;
- review only security checks that apply to the project;
- investigate authentication, authorization, business logic, injection, SSRF, files, supply chain, AI/MCP and other security surfaces;
- verify important candidates instead of reporting guesses;
- fix the root cause;
- add regression proof and retest;
- return a clear release decision.
See it work in 90 seconds
A small multi-tenant API with two candidate issues. One is a real cross-tenant read that a scanner walks past, because the endpoint does have an authorization check — it just checks the wrong thing. The other is f-string SQL that every pattern matcher flags and that is not exploitable at all.
Walkthrough, root cause, the two-line fix and the regression proof: examples/expense-api.
Or take the same test in your browser — ten cases, three of them decoys, no signup: Can you tell the real bug from the decoy?
Install
Recommended for Agent Skills-compatible coding agents:
Then open the repository you want to review in your coding agent. The skill installs instructions and data only — no executable code. The optional runtime below is a separate, explicit install.
A compact edition, sechelix-lite, is a single runtime-free review skill (about 200 lines plus
five references) for skill directories and hosts where a small context footprint matters. See
docs/distribution/awesome-copilot.md.
Use it
Full security audit
Copy this into your agent:
Fast security review
AI-built app launch audit
Use this before launching an AI-generated, agent-generated, rapidly prototyped, or vibe-coded application:
The launch profile covers practical pre-release failures around secrets, auth/authz, cross-user data, database/storage permissions, debug exposure, input validation, SQL/NoSQL injection, XSS/CSRF, uploads, traversal, SSRF, password reset, sessions/JWT, CORS, rate limiting, staging, default credentials, webhooks, payments/entitlements, IDOR/BOLA, sensitive logs, and production artifacts.
Review a pull request
Fix findings
More copy-paste workflows: Command Cookbook.
What should I ask SecHelix to do?
| Goal | Ask for |
|---|---|
| Full repository review | complete security audit |
| Quick first pass | security triage |
| AI-built/vibe-coded app before launch | AI-Built App Launch Audit |
| Broken access control | authorization / IDOR / BOLA audit |
| Login and sessions | authentication / session / OAuth audit |
| Input handling | injection / XSS / SSRF / files audit |
| Payments and workflows | business logic / race / idempotency audit |
| Dependencies and CI | supply chain / CI/CD audit |
| LLMs, agents and tools | AI / Agent / MCP security audit |
| A code change | PR security review |
| Existing verified issues | Fix Mode |
| Release decision | release gate |
| Shareable output | security report |
You do not need to memorize special slash commands. SecHelix is primarily a skill: tell the coding agent what security job you want done.
How the review works
A scanner match or model suspicion is treated as a candidate, not automatically as a vulnerability.
A strong finding should show the affected surface, attacker control or security boundary involved, reachability, impact, root cause, safe evidence, the fix, and regression/retest status.
What SecHelix does not claim
- It is not a certification.
PASSmeans the release-gate rules found no unresolved blocking condition in what was reviewed, not that the software has no vulnerabilities. - On real code it found 2 of 12 known CVEs. A blinded run against the vulnerable and patched
trees of 12 recent CVEs found 2 cleanly under the pre-registered rule, 3 with hand
adjudication, and no finding it marked
VERIFIEDwas one of the known defects (report). Precision isNOT_MEASURED. - The model still does the reasoning. SecHelix structures the review and labels unproven
claims as unproven rather than dropping them: in that run 92 of 106 findings were marked
LIKELY_BUT_UNPROVENorHYPOTHESIS. It does not make a model see a bug it cannot reason about. - Host support varies. Installation is verified for the Claude Code plugin, the Agent Skills CLI, the portable bundle and the curated Copilot CLI plugin; other hosts are documented paths (compatibility).
- Authorized targets only. It is not an internet scanner and ships no exploit payloads.
Optional CLI runtime
The Agent Skill works without the Python runtime. The runtime is optional and adds stored runs, coverage tracking, replayable evidence, reports, CI-friendly exit codes, and an MCP adapter.
Install it with:
uv tool install sechelix and python -m pip install sechelix are also supported.
Useful CLI commands
| Command | What it does |
|---|---|
sechelix doctor | Shows available components and reasoning executors |
sechelix audit . --executor claude-code | Runs an audit using Claude Code as the reasoning executor |
sechelix audit . --executor gemini-cli | Runs an audit using Gemini CLI as the reasoning executor |
sechelix runs | Lists saved runs and checks their integrity |
sechelix coverage | Shows what previous runs did not examine |
sechelix report | Renders the latest saved run |
sechelix replay <run_id> | Replays a recorded run offline and checks consistency |
sechelix mcp . | Serves the local MCP adapter over stdio |
Example:
sechelix audit .with the default--executor noneintentionally does not pretend to analyze code. Reasoning nodes are blocked and the run remains incomplete until a real executor is configured.
For all CLI flags:
Advanced runtime guide: V4 Runtime Quickstart.
GitHub Action
Outputs PASS, PASS_WITH_KNOWN_RISK, BLOCKED or INCOMPLETE, writes SARIF
for code scanning, and uploads the run as an artifact. The default
executor: none deliberately reports INCOMPLETE rather than a green check it
did not earn — configure a reasoning executor to get an actual review.
Full reference: GitHub Action.
MCP adapter
Related MCP Servers
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about SecHelix
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/sechelix)HTML Embed
<a href="https://allmcps.com/mcp/sechelix"><img src="https://allmcps.com/api/badge/sechelix?style=directory" alt="SecHelix on AllMCPs" /></a>