Agent-first code intelligence over MCP. AST for 7 languages. 20 tools. Offline.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
Not yet automatically verified
We haven't yet run this listing's install command through our automated sandbox check. This isn't a red flag — we're steadily working through the catalog.
Manual Client & Custom JSON ConfigExpand JSON ▾
Client Config & Setup
Choose your client or environment
Target File:
💡 Paste the JSON block into your client's configuration file under mcpServers, then restart the application.
Documentation Overview
projscan


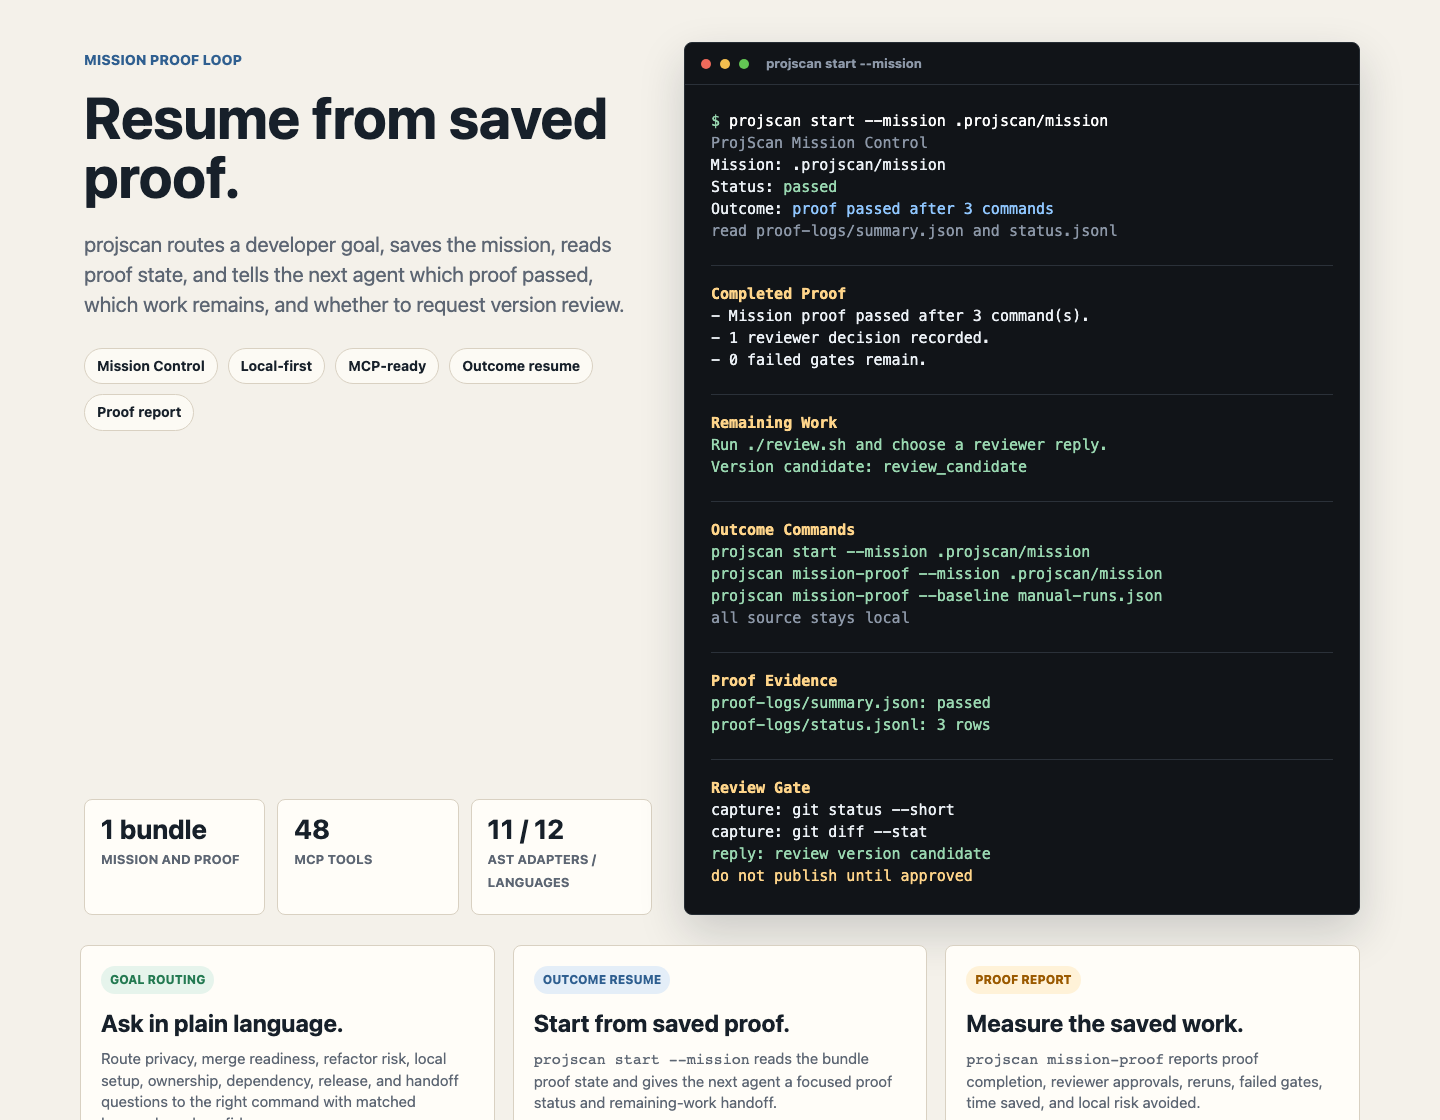
Local proof for AI-assisted engineering. projscan gives agents and engineers the repo context, risk checks, proof commands, and review gates they need before editing, handing off, or preparing a release candidate.
Install · Daily workflows · MCP Setup · Commands · Trust · Full Guide
Use It For
Use projscan when an agent asks one of these questions:
- Which files should I read before changing this feature?
- Which proof commands should I run before handoff?
- Which risks need fixes, reviewer attention, or release sign-off?
- Which risk should I fix first?
- Did the agent stay inside the approved change boundary?
projscan runs core scans on your machine. It respects .gitignore, keeps .env values out of scans unless you opt in, and exposes the same evidence through a CLI and a 51-tool MCP server. The language layer uses 11 AST adapters covering 12 named languages.
Install
Run without a global install:
Check the trust boundary first:
Daily workflows
Use these four workflows before scanning the full command catalog.
Before editing a feature
You get a cited change map, read-first files, likely touched files, blocked inputs, an executable Proof Contract, and a before-edit proof gate. Agent-permission intents route to projscan prove, so start can hand the next agent a contract path instead of a broad checklist.
Success criteria: the agent can name the files to read first, the likely files to touch, the forbidden files to avoid, and the proof commands to run before editing.
Verified change workflow
The command path is start -> prove -> run -> changed. Make the bounded edit after the contract exists and before prove --run. start chooses the contract workflow. prove --intent writes .projscan/proof-contract.json only when --save-contract is present. prove --run -- <command...> executes a local proof command, records the exit code, captures a redacted log, and fingerprints the current changed files. prove --record-command remains available for imported CI or external evidence when projscan did not run the command. prove --changed checks the current working tree against the contract and local ledger.
You get a Proof Contract before edits and a Proof Receipt after edits. The contract names allowed files, forbidden files, risky contracts, likely tests, missing regression-test evidence, proof commands, safe change shape, rollback, confidence, reviewer guidance, and proofRequirements for each risk surface. The receipt checks the real working tree against that contract and classifies changed files as allowed production, expected tests, documentation, generated proof artifacts, config/security drift, forbidden touches, or unexpected production. The receipt reports proof replay status, Proof Sufficiency, risk delta, commit readiness, and a reviewer checklist.
Sibling Baseframe harness directories (.agentloop/, .agentflight/) are classified as harness evidence, not scope drift: AgentLoopKit and AgentFlight write session state, task status transitions, and verification reports there as part of their sanctioned workflows, so those writes stay informational in the receipt and never trip forbiddenTouched, block commit readiness, or stop the review gate. Auto-generated contracts no longer list them in forbiddenFiles, receipts ignore those entries in contracts saved by older versions, and Team Proof Recipe forbiddenFiles entries are read the same way. To forbid production paths, keep using forbiddenFiles or Team Proof Recipes for non-harness locations.
Dependency-change intents keep their own scope executable: when prove --intent describes a dependency or tooling version change (for example "upgrade projscan to 5.0.1"), the generated contract places package.json and package-lock.json in allowedFiles instead of forbiddenFiles. Unrelated intents keep the manifests forbidden by default. Contract artifacts are restricted to .projscan/proof-contract.json or .projscan/proof-contracts/<name>.json inside the project root; --save-contract and --contract reject other paths.
Proof Replay records command, exit code, duration, changed-file fingerprint, redacted summary, log path, and source in .projscan/proof-ledger.jsonl. Executed proof logs stay under .projscan/proof-logs/. Ledger matching normalizes package-runner prefixes, so npx projscan assess --mode fix-first --format json, pnpm exec projscan ..., and node_modules/.bin/projscan ... all satisfy a required projscan assess --mode fix-first --format json. prove --changed marks proof as passed, missing, failed, partial, or stale. The receipt JSON includes proofReplay with a replay timeline, changedAfterProof, replay command, and local receipt fingerprint. If the agent edits new files after proof ran, the receipt says the proof is stale before a reviewer reads the diff.
Proof Sufficiency estimates whether the local ledger covers each changed surface. proofSufficiency marks rows as strong, adequate, weak, missing, stale, or failed, then lists the exact gaps reviewers need to resolve.
Team Proof Recipes let a repo encode required proof for sensitive paths in proofRecipes; when a matching recipe is configured, prove --intent adds that recipe's commands, reviewers, and forbidden files to the Proof Contract. prove --changed and projscan evidence-pack --pr-comment then show missing recipe proof, required reviewers, and recipe drift in the Proof Receipt. The recipe does not run proof commands by itself; use prove --run -- <command...> or prove --record-command to add evidence to the local ledger.
Saved contracts are the source of truth for prove --changed; update the contract when a team recipe changes.
Every prove report includes verifiedWorkflow, a compact JSON summary for agents and MCP clients. It names the phase, next action, next command, scope status, proof status, proof sufficiency status, risk delta direction, reviewer decision, and stale/missing/failed proof flags.
Related MCP Servers
Adoption & maintenance
Factual signals from GitHub, npm, and our automated checks — not a rating.
GitHub stars
4
Stargazers on the source repository.
Last commit
2mo ago
Most recent push to the default branch.
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about Projscan
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/projscan)HTML Embed
<a href="https://allmcps.com/mcp/projscan"><img src="https://allmcps.com/api/badge/projscan?style=directory" alt="Projscan on AllMCPs" /></a>Technical Specs & Signals
CategoryDeveloper Tools
11/15 checks healthy over the last 45d
39Quality signal: Fair · 39/100How this signal is calculated ▾
Server availabilityNot measured
Not scored for repo-hosted servers — we can't reach the running server, only its GitHub page. Hosted MCP endpoints are health-checked live.
Verified ownership10/20
Documentation & tools15/30
Adoption & activity4/15
Community engagement0/10
A guidance signal from public completeness & health data — not a user rating. New listings start lower and rise as they add docs, get verified, and grow adoption. Signals we can't observe for a listing are skipped, not counted against it.
Supply-chain signal
No high-severity advisories surfaced by our automated scan.
Critical 0High 0Medium 0Low 0
Scanned 6d ago via OSV.dev · projscan (npm)
Own this project?
This directory is pre-filled from public sources. Claim via GitHub README, site badge, or DNS TXT to unlock edit access and the Official badge — proof is checked automatically, then reviewed by our team.
Free dofollow backlink: add your website and place the AllMCPs badge on it — no claim needed. We detect it automatically and keep it verified as long as the badge stays live.
Claim & get free dofollowShare & Embed
Add our SVG badge (dark/light directory styles) or embeddable widget to your site.