MCP runtime security proxy. Blocks dangerous AI agent tool calls with a policy engine.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
Not yet automatically verified
We haven't yet run this listing's install command through our automated sandbox check. This isn't a red flag — we're steadily working through the catalog.
Manual Client & Custom JSON ConfigExpand JSON ▾
Client Config & Setup
Choose your client or environment
Target File:
💡 Paste the JSON block into your client's configuration file under mcpServers, then restart the application.
Documentation Overview
MCP Seatbelt — Runtime Guardrails for AI Agent Tools
Block dangerous MCP tool calls at the protocol layer. Scan, proxy, enforce.




Part of the MCP Security Platform. Scan before you trust with mcp-observatory (236★), then enforce at runtime with mcp-seatbelt. 📄 Read the technical whitepaper.
🌐 Website: kryptosai.github.io/mcp-seatbelt — demo, comparison, pricing
The Problem
AI coding agents (Cursor, Claude, VS Code, ChatGPT, Windsurf, and others) connect to MCP servers that expose file systems, shell interpreters, network access, and environment variables. Static scanners tell you you're exposed — but they act after the fact. By the time a scanner flags a risky server, the agent may have already run a destructive command, exfiltrated credentials, or reached out to an untrusted endpoint.
MCP Seatbelt adds a runtime enforcement layer. It acts as a policy proxy between the agent and every MCP server, evaluating each JSON-RPC tool call against rules you control and denying dangerous requests before they reach the upstream. It does not operate at the TCP level — it inspects and gate-checks every call at L7 (the MCP protocol layer) before forwarding.
What It Does
Detection & Proxy
-
Detects MCP configs across 8 clients — Automatically discovers MCP server configurations from Cursor, Claude Desktop, VS Code (user + workspace), ChatGPT Desktop, Codex, JetBrains IDEs (IntelliJ, PyCharm, WebStorm, etc.), Windsurf, and project-local files (
.mcp.json,.mcp/config.json). No manual wiring required. -
Runtime proxy with policy enforcement — Starts a transparent JSON-RPC 2.0 proxy on port 9420. Every tool call, resource access, and prompt request is intercepted, evaluated against your policy, and allowed, denied, warned, or redacted. Three modes:
default-deny(zero-trust),allowlist(whitelist known-good), andaudit(log only, no blocking). -
13 built-in risk rules — Covers shell interpreters (
bash,sh,zsh,python,node), sandbox bypass (--no-sandbox,--disable-web-security), credential exposure in environment variables, Docker privileged containers, raw network tools (curl,nc,telnet), process spawning, destructive filesystem operations, remote URL access, risky package runners (npx,uvx), privilege escalation (sudo,chmod), and sensitive filesystem paths. -
Policy engine with time-windowed rules, learning mode, rule inheritance, and context awareness — Rules support regex pattern matching, exact-match, and substring containment. Restrict tool access by day of week and hour range (
timeWindow). Condition rules on client identity or request rate (contextCondition). Policies canextendparent templates. Theauditmode serves as a learning mode: run it to observe actual tool usage before switching toenforce. -
Live dashboard, SARIF reports, CI/CD integration, and observatory bridge — A real-time HTML dashboard shows request stats, block rates, connected clients, and recent blocked calls. Generate SARIF 2.1.0 reports for GitHub Code Scanning. Import security findings from mcp-observatory and automatically convert them to policy rules.
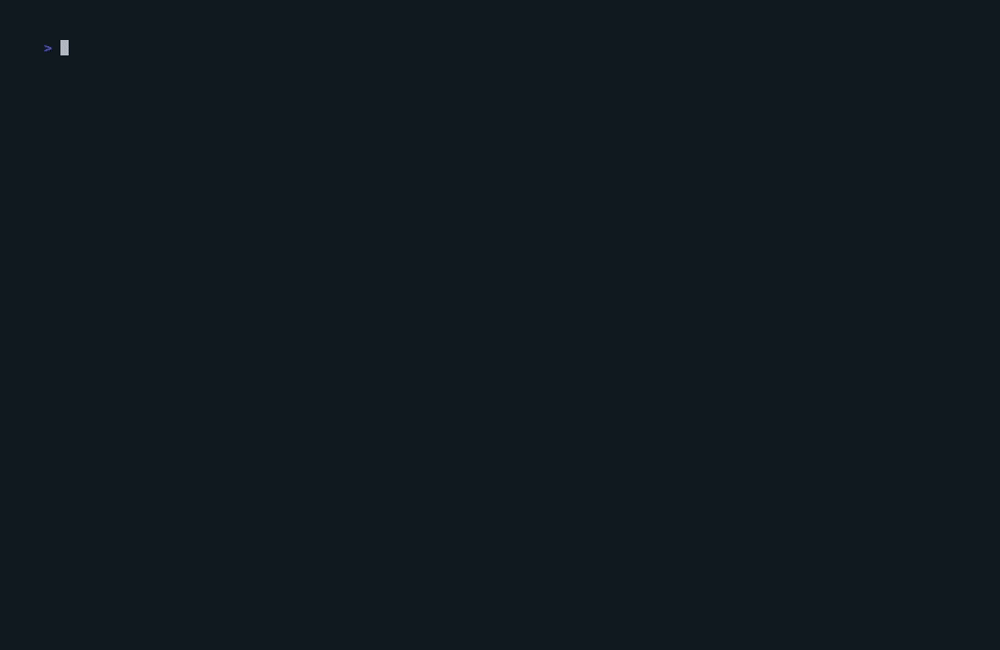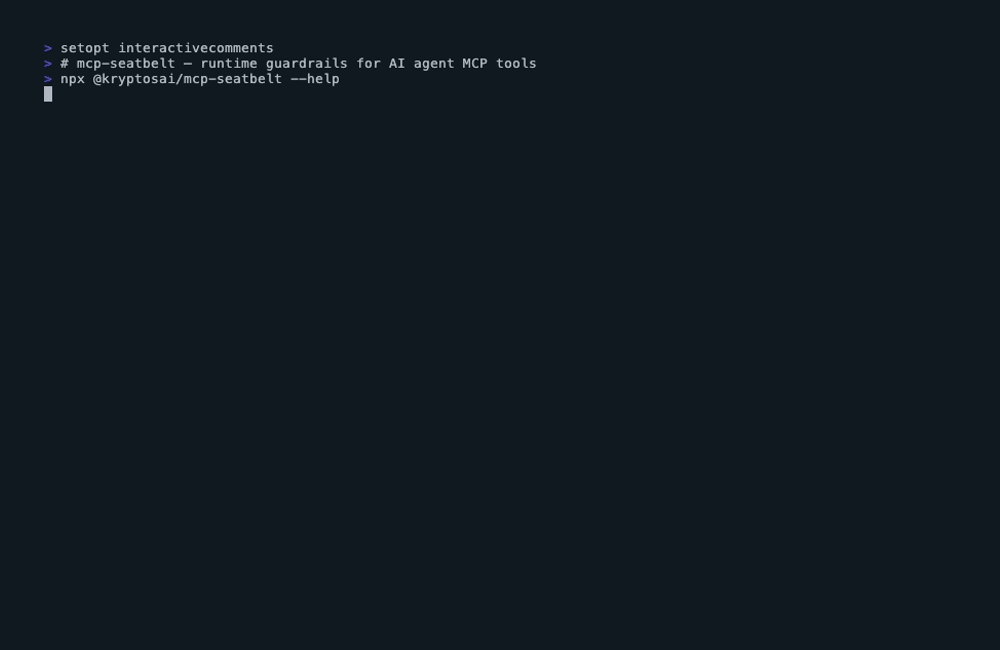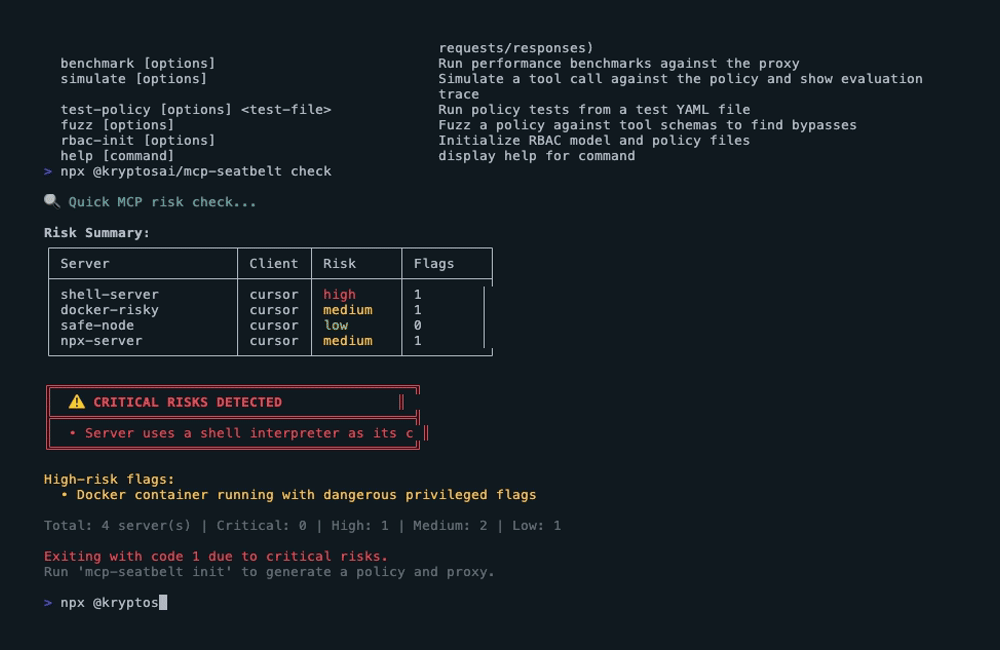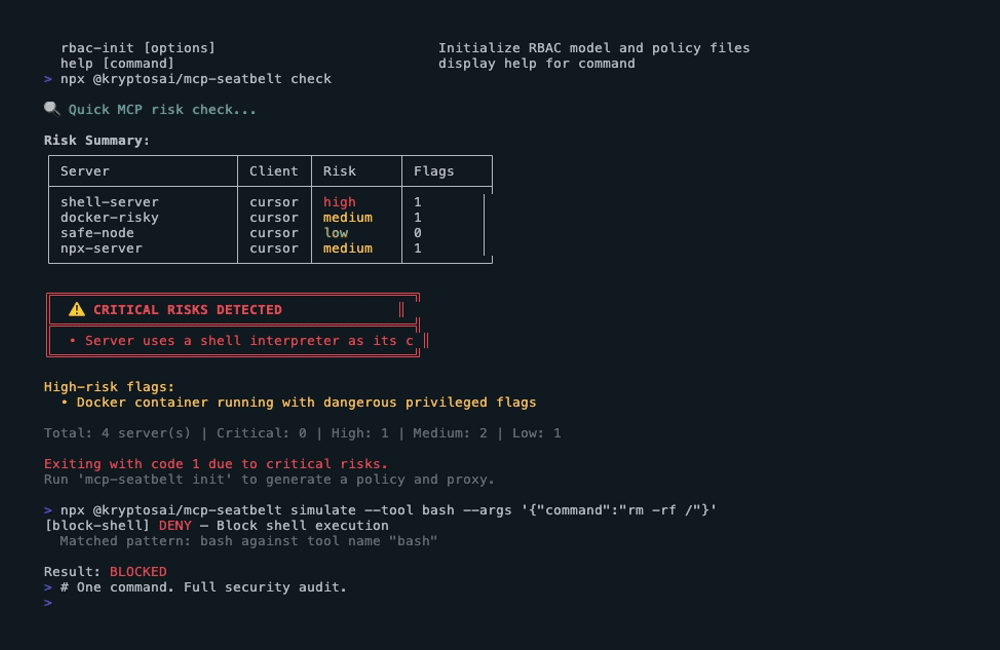
mcp-seatbelt checkexits non-zero in CI when critical risks are detected. -
Per-call timeouts — Hung tool calls are killed and return a clean JSON-RPC error instead of a raw 503. Configurable per-rule (10s for shell commands, 60s for safe tools).
Advanced Security
- OWASP LLM Top 10 mapping — Every blocked call is tagged with OWASP categories (LLM01 Prompt Injection, LLM06 Excessive Agency, etc.)
- Compliance framework mapping — Policy rules carry SOC2, HIPAA, GDPR, ISO 27001, and PCI-DSS control tags
- Multi-step attack chain detection — XState-based state machine tracks call sequences: recon → execution → persistence → exfiltration
- Honeytoken injection & detection — Plants decoy credentials (AWS keys, GitHub tokens, DB URLs) in tool responses, alerts on access
- Forensic session capture — Records full request/response pairs as
.mcpcap.jsonfor incident analysis - Schema-aware argument validation — Validates tool arguments against declared JSON Schemas, detects path traversal and injection
- Threat intelligence integration — Queries ThreatFox IOC database for IP/domain reputation checks
- Input fuzzing — Generates edge-case payloads against policy rules to find bypasses
- Role-based access control — Per-agent permissions with casbin. Admin can execute all tools, agents get scoped access
- Response DLP — Scans upstream responses for secret patterns (API keys, tokens, private keys) and redacts them
Quick Start
On first run, init creates .mcp-seatbelt/policy.yml (your editable ruleset) and .mcp-seatbelt/risk-report.md (a summary of every server and its risk flags). The proxy starts in audit mode by default — observe actual tool usage, then switch to enforce when ready.
Docker
Images are automatically built and published on every release via GitHub Actions.
GitHub Action
Run MCP Seatbelt as a CI security gate with the official GitHub Action — it checks detected MCP configs, simulates your policy against representative tool calls, and fails the build on critical risks.
CI/CD Integration
See action.yml for all inputs, outputs, and enforcement options.
How It Works
- Proxy — Listens for inbound JSON-RPC 2.0 requests from the AI agent. Manages server registration, proxied URL routing, and connection lifecycle.
- Policy Engine — Evaluates each request against the loaded policy. Checks tool name, arguments, and description against rules. Returns
allow,deny,warn, orredactwith reasons. - Interceptor — Applies the engine's decision. Allowed calls are forwarded. Denied calls receive an MCP error response. Warned calls proceed but are logged.
redactreplaces argument values matching credential patterns with***. - Transport Client — Forwards allowed requests to the real upstream MCP server and streams responses back to the agent.
The proxy never returns a raw upstream error to the agent. If a call exceeds its timeout, the child process is killed and the agent receives a clean error message — no 503s, no hanging connections.
Related MCP Servers
Adoption & maintenance
Factual signals from GitHub, npm, and our automated checks — not a rating.
GitHub stars
3
Stargazers on the source repository.
npm downloads
1.1k
Package downloads in the last 30 days.
Last commit
1mo ago
Most recent push to the default branch.
Directory activity
1 views
Config copies, upvotes, and views on AllMCPs.
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about MCP Seatbelt
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/mcp-seatbelt)HTML Embed
<a href="https://allmcps.com/mcp/mcp-seatbelt"><img src="https://allmcps.com/api/badge/mcp-seatbelt?style=directory" alt="MCP Seatbelt on AllMCPs" /></a>Technical Specs & Signals
CategorySecurity
3/6 checks healthy over the last 46d
44Quality signal: Fair · 44/100How this signal is calculated ▾
Server availabilityNot measured
Not scored for repo-hosted servers — we can't reach the running server, only its GitHub page. Hosted MCP endpoints are health-checked live.
Verified ownership10/20
Documentation & tools16/30
Adoption & activity7/15
Community engagement0/10
A guidance signal from public completeness & health data — not a user rating. New listings start lower and rise as they add docs, get verified, and grow adoption. Signals we can't observe for a listing are skipped, not counted against it.
Supply-chain signal
No high-severity advisories surfaced by our automated scan.
Critical 0High 0Medium 0Low 0
Scanned 6d ago via OSV.dev · @kryptosai/mcp-seatbelt (npm)
Own this project?
This directory is pre-filled from public sources. Claim via GitHub README, site badge, or DNS TXT to unlock edit access and the Official badge — proof is checked automatically, then reviewed by our team.
Free dofollow backlink: add your website and place the AllMCPs badge on it — no claim needed. We detect it automatically and keep it verified as long as the badge stays live.
Claim & get free dofollowShare & Embed
Add our SVG badge (dark/light directory styles) or embeddable widget to your site.