Infra Lens MCP
SSH Linux metrics, baselines, anomaly detection, and plain-English infrastructure explanations.
Install Infra Lens MCP
Pick your client, then add it in one click or paste the config.
~/Library/Application Support/Claude/claude_desktop_config.json{
"mcpServers": {
"infra-lens-mcp": {
"command": "npx",
"args": [
"-y",
"infra-lens-mcp"
]
}
}
}
Settings → Developer → Edit Config, merge this into mcpServers, then fully quit and reopen Claude Desktop.
Install not yet sandbox-tested— we haven't run this command through our automated sandbox yet. Not a red flag; we're working through the catalog.
Overview
Tools10
What Infra Lens MCP lets your agent do. Expand a tool for its parameters.
Security & health
What it can reach and how reliably it runs — from our own checks, not the maintainer’s claims.
Recent health check succeeded.
Supply-chain signal
No high-severity advisories surfaced by our automated scan.
Scanned 13d ago via OSV.dev · infra-lens-mcp (npm)
Adoption & maintenance
Factual signals from GitHub, npm, and our automated checks — not a rating.
From the project README
infra-lens-mcp
Explain Linux incidents over SSH with baseline-aware MCP tooling.
A TypeScript MCP server for live Linux diagnostics, local SQLite history,
review-first incident workflows, and secure observability exports.





Documentation · Usage · Architecture · Security · Governance · Roadmap · Support · Releases

infra-lens-mcp connects to Linux hosts over SSH, captures bounded live metrics, stores observations and approved baselines in local SQLite, explains anomalies, and produces review-first incident artifacts. The npm package and signed container are release-ready; public connector publication remains intentionally blocked until an external OAuth/HTTPS deployment is verified.
Demo
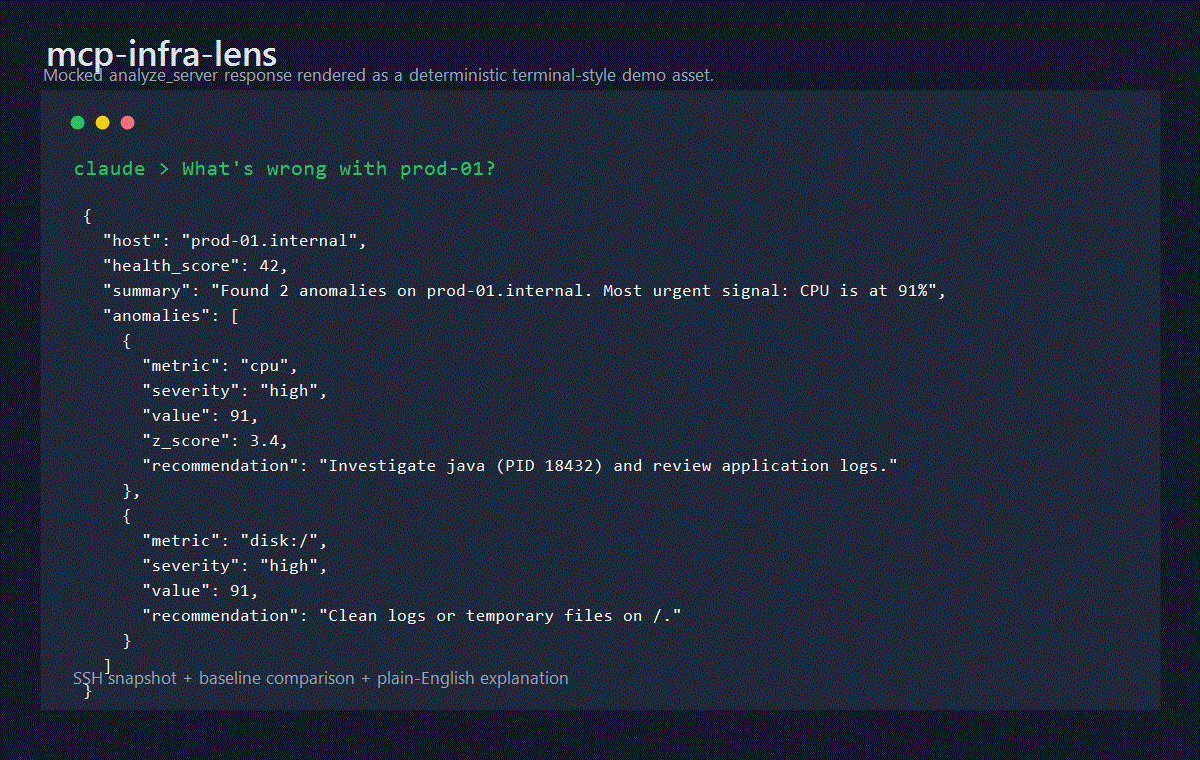
See the MCP 2025-11-25 compliance matrix for current protocol support, delegated behavior, and connector publication constraints.
Tools
| Tool | Purpose |
|---|---|
analyze_server | Analyze a bounded sampled window with progress/cancellation support, then store only the completed observation |
analyze_server_snapshot | Analyze and store one immediate snapshot without a sampling delay |
snapshot | Store a point-in-time observation without anomaly analysis |
record_baseline | Save a labeled healthy-state sample |
compare_to_baseline | Compare current state with a named baseline |
get_history | Return CPU, memory, or load history from SQLite |
inspect_host_capabilities | Check required Linux commands and proc files before collection |
plan_remediation | Propose evidence-backed, approval-required remediation without executing changes |
draft_incident_report | Draft an incident report and postmortem from persisted observations |
compare_incident_windows | Compare adjacent windows for one host or the same window across two hosts |
All tools return both readable JSON text and MCP structuredContent validated by declared outputSchema definitions, so clients and agents can consume responses without parsing the text block. Collection tools include a warnings array when optional sections cannot be collected but a partial snapshot is still usable. Use analyze_server_snapshot for interactive checks; use analyze_server only when a sampled window is required. Sampled analysis emits MCP progress when the client supplies a progress token and never persists a cancelled partial run.
Requirements
- Node.js 24 LTS for CI, Docker, and release workflows
- Node.js 22 or newer for package runtime compatibility
- pnpm 11.15.1 through Corepack for development installs
- Linux SSH targets with
/proc,free,df,ps, anduname - Strict SSH host verification through
known_hostsor pinned SHA256 host keys
Quick Start
Run the stdio MCP server from npm:
npx -y infra-lens-mcp
Desktop MCP client style configuration:
{
  "mcpServers": {
    "infra-lens": {
      "command": "npx",
      "args": ["-y", "infra-lens-mcp"],
      "env": {
        "INFRA_LENS_DB": "/Users/you/.infra-lens-mcp/metrics.db"
      }
    }
  }
}
Local development:
corepack enable
corepack prepare pnpm@11.15.1 --activate
pnpm install --frozen-lockfile
pnpm run build
node dist/mcp.js
Configuration
Transport is selected by the executable entry point, not by an environment variable: npx -y infra-lens-mcp or node dist/mcp.js starts stdio, while node dist/server-http.js starts Streamable HTTP.
| Variable | Default | Description |
|---|---|---|
INFRA_LENS_DB | ~/.infra-lens-mcp/metrics.db | SQLite database path |
INFRA_LENS_RETENTION_DAYS | 30 | Snapshot retention in days; 0 disables automatic pruning |
MCP_HTTP_HOST | 127.0.0.1 | HTTP bind host. HOST remains a deprecated alias |
MCP_HTTP_PORT | 3000 | HTTP bind port. PORT remains a deprecated alias |
MCP_HTTP_ENDPOINT_PATH | /mcp | Canonical Streamable HTTP MCP endpoint path |
MCP_HTTP_ALLOWED_ORIGINS | unset | Comma-separated allowed Origin values |
MCP_HTTP_ALLOWED_HOSTS | unset | Comma-separated allowed Host values |
MCP_HTTP_AUTH_MODE | none | none, bearer, or oauth-gateway; oauth is accepted as a compatibility alias |
MCP_HTTP_BEARER_TOKEN | unset | Local/dev bearer fallback token |
MCP_HTTP_OAUTH_GATEWAY_HEADER | x-infra-lens-gateway-auth | Header injected by a trusted OAuth gateway |
MCP_HTTP_OAUTH_GATEWAY_SECRET | unset | Shared backend secret required for oauth-gateway mode |
MCP_HTTP_BODY_LIMIT_BYTES | 1048576 | Maximum JSON request body size |
MCP_HTTP_REQUEST_TIMEOUT_MS | 30000 | Maximum time to receive and handle an HTTP request before the socket is closed |
MCP_HTTP_MAX_CONCURRENT_REQUESTS | 100 | Maximum concurrent HTTP requests accepted by the Node process |
MCP_HTTP_RATE_LIMIT_PER_MINUTE | 0 | Optional per-client in-memory rate limit; 0 disables it |
MCP_HTTP_AUTHORIZATION_SERVERS | unset | OAuth authorization server metadata URLs |
MCP_PROFILE | full | full, remote-safe, chatgpt, or claude |
MCP_SSH_STRICT_HOST_CHECKING | true | Strict host key verification toggle |
MCP_SSH_KNOWN_HOSTS | ~/.ssh/known_hosts | Known hosts file |
MCP_SSH_ALLOWED_HOSTS | unset | Exact host/IP or IPv4 CIDR allowlist; required for remote-safe profiles and enforced in full profile when set |
MCP_SSH_ALLOWED_USERS | unset | Optional comma-separated SSH username allowlist |
MCP_SSH_ALLOWED_PORTS | unset | Optional comma-separated SSH port allowlist |
MCP_SSH_MAX_SESSIONS_PER_HOST | 0 | Optional active SSH session cap per host:port; 0 disables it |
MCP_SSH_MAX_CONNECTION_ATTEMPTS_PER_MINUTE | 0 | Optional SSH connection-attempt cap per host:port per minute; 0 disables it |
MCP_DB_PATH from older examples is not used; use INFRA_LENS_DB.
SSH Security
Strict host key checking is enabled by default. Provide either:
- a
hostKeySha256value in the connection input, such asSHA256:... - a
knownHostsPathin the connection input MCP_SSH_KNOWN_HOSTSpointing at an OpenSSHknown_hostsfile
Raw passwords, private keys, and passphrases are accepted only in the default full profile for trusted local MCP contexts. remote-safe, chatgpt, and claude profiles reject raw SSH credentials in tool input and require MCP_SSH_ALLOWED_HOSTS. Production SSH policy can also restrict exact hosts or IPv4 CIDR ranges, users, ports, per-host active sessions, and per-host connection attempts.
Process command arguments are not collected by the default process command. Secret-like values in process data, SSH errors, and logs are redacted before storage or output.
HTTP Transport
Reviews
No reviews yet — be the first to share how it worked for you.
Frequently Asked Questions about Infra Lens MCP
Related MCP servers
Add a badge to your READMEShow it’s listed — live SVG, Markdown or HTML.
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
[](https://allmcps.com/mcp/infra-lens-mcp)<a href="https://allmcps.com/mcp/infra-lens-mcp"><img src="https://allmcps.com/api/badge/infra-lens-mcp?style=directory" alt="Infra Lens MCP on AllMCPs" /></a>