Webhook signature-verification audit. Stripe, GitHub, Shopify, Twilio +17. Local. Deterministic.
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
Not yet automatically verified
We haven't yet run this listing's install command through our automated sandbox check. This isn't a red flag — we're steadily working through the catalog.
Manual Client & Custom JSON ConfigExpand JSON ▾
Client Config & Setup
Choose your client or environment
Target File:
💡 Paste the JSON block into your client's configuration file under mcpServers, then restart the application.
Documentation Overview

The only scanner laser-focused on webhook signature verification.
Local. Deterministic. Zero-network. JS/TS + Python + PHP + Go. Five minutes from npx to fix.




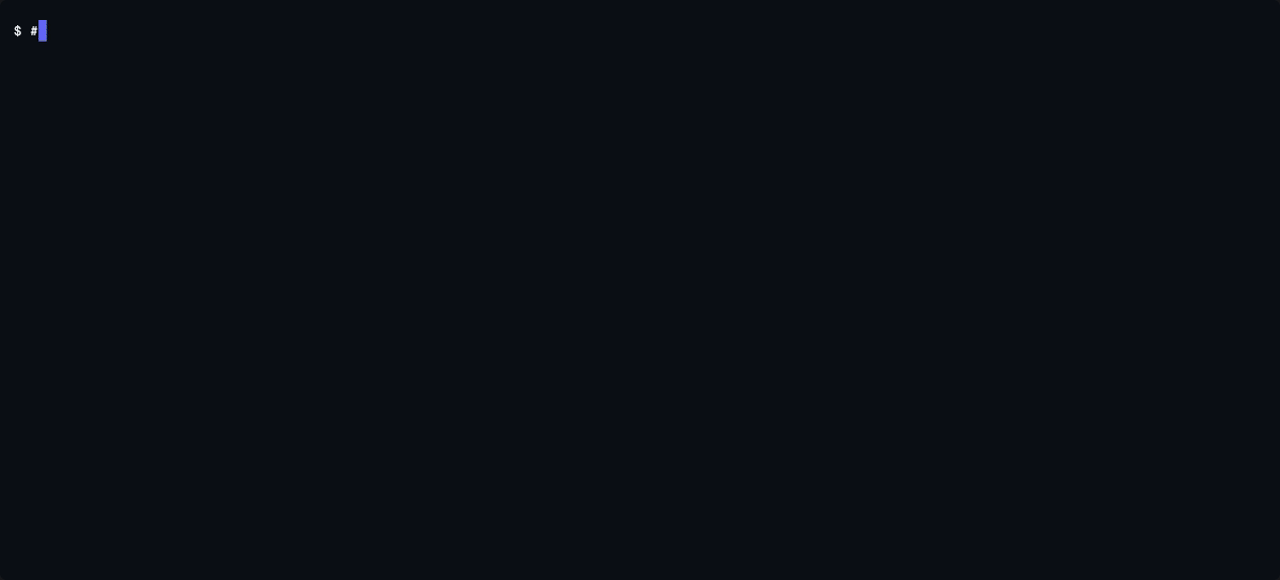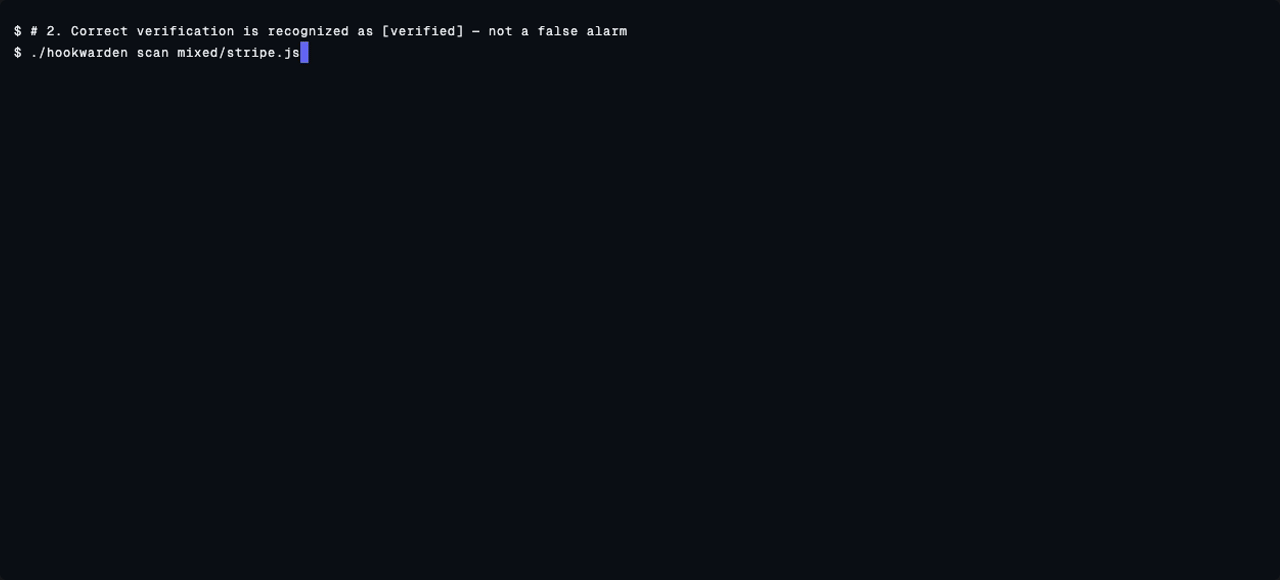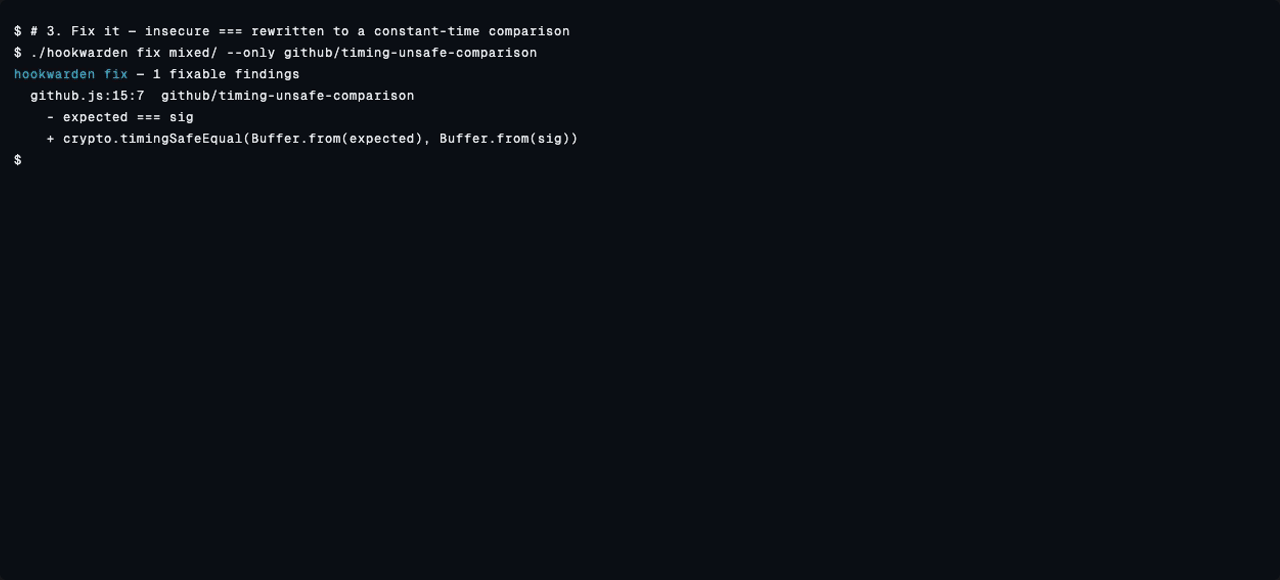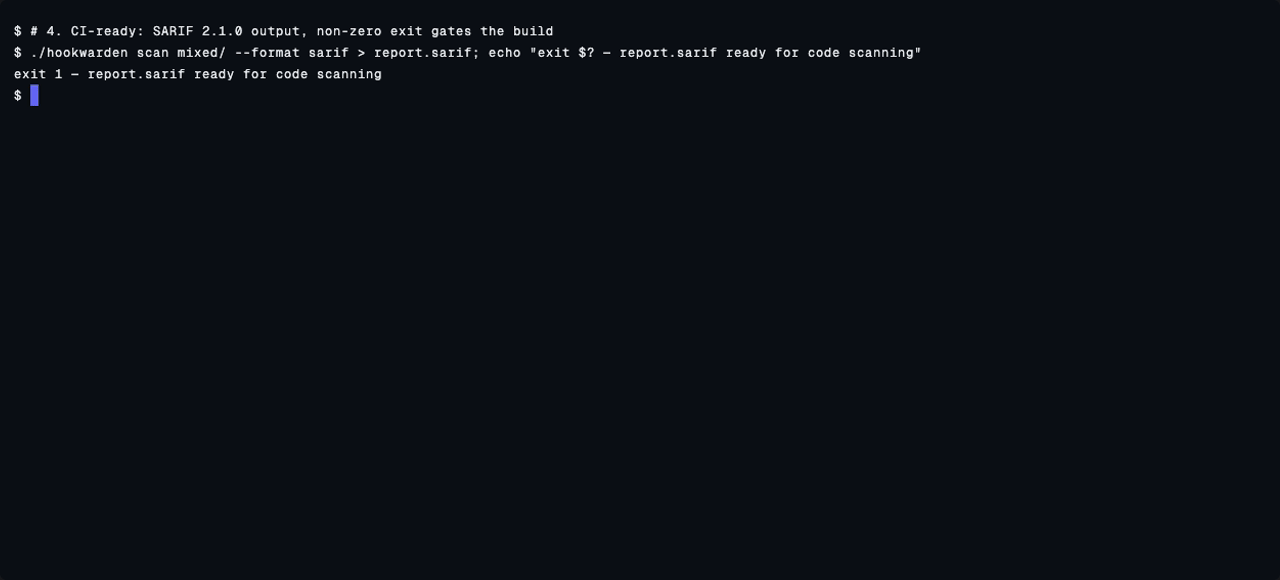
No traffic leaves your machine. No telemetry. No SaaS sign-up required.
📖 Full documentation: docs.hookwarden.dev
Found in the wild
Every Sunday at 22:00 UTC, this repo's CI runs hookwarden against 45 popular open-source projects — currently cal.com, documenso, formbricks, twenty, plane, unkey, typebot, papermark (full target list, combined ★190k+) — to prove the scanner works on real production code.
Latest sweep — 2026-06-09 · 20/45 projects clean (zero critical/high)
| Provider | 🚨 critical | ⚠️ high | 🟡 manual-review | Rules that fired |
|---|---|---|---|---|
| n8n integrations | 81 | 0 | 0 | n8n/missing-signature-verification (×78)n8n/raw-body-misuse (×3) |
| Slack integrations | 7 | 1 | 0 | slack/missing-signature-verification (×7)slack/verify-after-side-effect (×1) |
| Standard Webhooks integrations | 7 | 0 | 0 | standardwebhooks/missing-signature-verification (×3)standardwebhooks/raw-body-misuse (×4) |
| Stripe integrations | 6 | 0 | 0 | stripe/hardcoded-secret-prefix (×2)stripe/missing-signature-verification (×4) |
| GitHub integrations | 0 | 0 | 0 | — |
| Shopify integrations | 0 | 0 | 0 | — |
| Square integrations | 0 | 0 | 0 | — |
| Twilio integrations | 0 | 0 | 0 | — |
These are bugs in the webhook handlers that receive provider events — flaws in the integrating projects' integration code, not in the providers' own SDKs or services.
Coverage note: the engine couldn't parse 238 files across the corpus (broken syntax or language features the parser doesn't model). Those are scan-coverage diagnostics — not handler bugs — and are excluded from the table above.
Hookwarden checks 11 rule classes across 21 providers — most of the corpus handles webhooks correctly, hence the short list. The full rule catalog lives in the docs.
Per-target findings are never published before responsible disclosure — see methodology. To run the same scan against your own code:
Why
Every dollar of fraud that flows through a webhook starts with a verification bug — and verification bugs hide in plain sight.
A handler that accepts an unsigned payload, compares HMACs with ==, or skips the signature check on a ?test=true path silently routes attacker traffic into your business logic. The bug is one line in a 50K-line app, and it looks plausible — not the shape general-purpose SAST tools are tuned to flag. They were built for SQL injection and prototype pollution; webhook verification falls between their default rule packs.
hookwarden does one thing. It walks your repo, parses every webhook handler across 11 frameworks, and labels each one verified, not-verified, or manual-review — with the exact file, line, and a fix quoted from provider docs. The catalog (21 named providers — Stripe, GitHub, Shopify, Slack, Twilio, Square, Sentry, Zendesk, DocuSign, PagerDuty, Notion, Auth0, HubSpot, Intercom, Linear, Zoom, Calendly, Bitbucket, Mailchimp, Postmark, plus Standard Webhooks conformant providers like Clerk, Resend, Mux) encodes signature quirks no generic scanner has the surface area to know: Stripe's 5-minute timestamp tolerance, Slack's v0:${ts}:${body} scheme, Twilio's SHA-1 outlier.
The three-state verdict is not a hedge. manual-review is what you get when hookwarden can't prove safety or unsafety from the source alone — a handler inside a middleware chain the analyzer couldn't unroll, say. It's how the false-positive rate stays honest (<5%, measured against a 200-repo OSS corpus). A tool that reports every gray area as a bug isn't a security tool; it's noise. → How the verdict works
Install
hookwarden is a CLI, not a library — run it with
npx hookwarden scan .or install globally withnpm i -g hookwarden. (The plainnpm i hookwardenthat npm auto-suggests on the package page installs it as a local dependency, which isn't what you want for a command-line tool.)
Or install natively:
| OS | Recommended | Alternates |
|---|---|---|
| Linux | brew install Hookwarden/tap/hookwarden | npm i -g hookwarden · pip install hookwarden · direct binary |
| macOS | brew install Hookwarden/tap/hookwarden | npm i -g hookwarden · npx hookwarden |
| Windows | scoop bucket add hookwarden https://github.com/Hookwarden/scoop-bucket && scoop install hookwarden | npm i -g hookwarden · pip install hookwarden |
Node 22+ is required for the npm/npx/macOS-brew paths; the standalone binaries (Linux x64/arm64, Windows x64) bundle the runtime. Direct binary downloads are intentionally unsigned (Gatekeeper / SmartScreen will warn) — prefer brew / scoop / npm / pip, which verify by SHA-256. → Install guide
Update
| Channel | Command |
|---|---|
| brew (macOS/Linux) | brew upgrade hookwarden |
| scoop (Windows) | scoop update hookwarden |
| npm (global) | npm i -g hookwarden@latest |
| pip | pip install -U hookwarden |
| npx (no install) | npx hookwarden@latest scan . — @latest bypasses the npx cache |
| direct binary | re-download from Releases |
Rule pack versions move with the CLI (engine, rules, and CLI ship as a fixed group — 0.7.5 everywhere). Pin in CI with npx hookwarden@0.7.5 scan . if you want byte-stable verdicts across runs.
Quickstart
--diff-only, --provider stripe,github (phased rollout), --include/--exclude globs, --strict-suppressions, repo-level hookwarden.config.yaml, and more: npx hookwarden --help and the CLI docs.
Git history scan (--history)
By default scan only looks at your working tree. --history also walks the
git history — including files that were committed then deleted before HEAD —
so a secret that was force-pushed away is still found. It's off by default and
bounded to the last 1000 commits; narrow it with --since <ref|date>:
Related MCP Servers
Adoption & maintenance
Factual signals from GitHub, npm, and our automated checks — not a rating.
GitHub stars
1
Stargazers on the source repository.
npm downloads
228
Package downloads in the last 30 days.
Last commit
1mo ago
Most recent push to the default branch.
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about Hookwarden — Webhook Integrity
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/hookwarden-webhook-integrity)HTML Embed
<a href="https://allmcps.com/mcp/hookwarden-webhook-integrity"><img src="https://allmcps.com/api/badge/hookwarden-webhook-integrity?style=directory" alt="Hookwarden — Webhook Integrity on AllMCPs" /></a>Technical Specs & Signals
CategoryCommunication
15/15 checks healthy over the last 46d
41Quality signal: Fair · 41/100How this signal is calculated ▾
Server availabilityNot measured
Not scored for repo-hosted servers — we can't reach the running server, only its GitHub page. Hosted MCP endpoints are health-checked live.
Verified ownership10/20
Documentation & tools16/30
Adoption & activity5/15
Community engagement0/10
A guidance signal from public completeness & health data — not a user rating. New listings start lower and rise as they add docs, get verified, and grow adoption. Signals we can't observe for a listing are skipped, not counted against it.
Supply-chain signal
No high-severity advisories surfaced by our automated scan.
Critical 0High 0Medium 0Low 0
Scanned 2d ago via OSV.dev · hookwarden (npm)
Own this project?
This directory is pre-filled from public sources. Claim via GitHub README, site badge, or DNS TXT to unlock edit access and the Official badge — proof is checked automatically, then reviewed by our team.
Free dofollow backlink: add your website and place the AllMCPs badge on it — no claim needed. We detect it automatically and keep it verified as long as the badge stays live.
Claim & get free dofollowShare & Embed
Add our SVG badge (dark/light directory styles) or embeddable widget to your site.