Haldir README
The full upstream README, mirrored here for reference. Install config, tool schemas, adoption signals, and an original overview live on the Haldir listing page.
Haldir
Scoped permissions, spend caps, an encrypted vault, and an audit log that can prove it wasn't edited — for AI agents that call tools, move money, and read secrets.


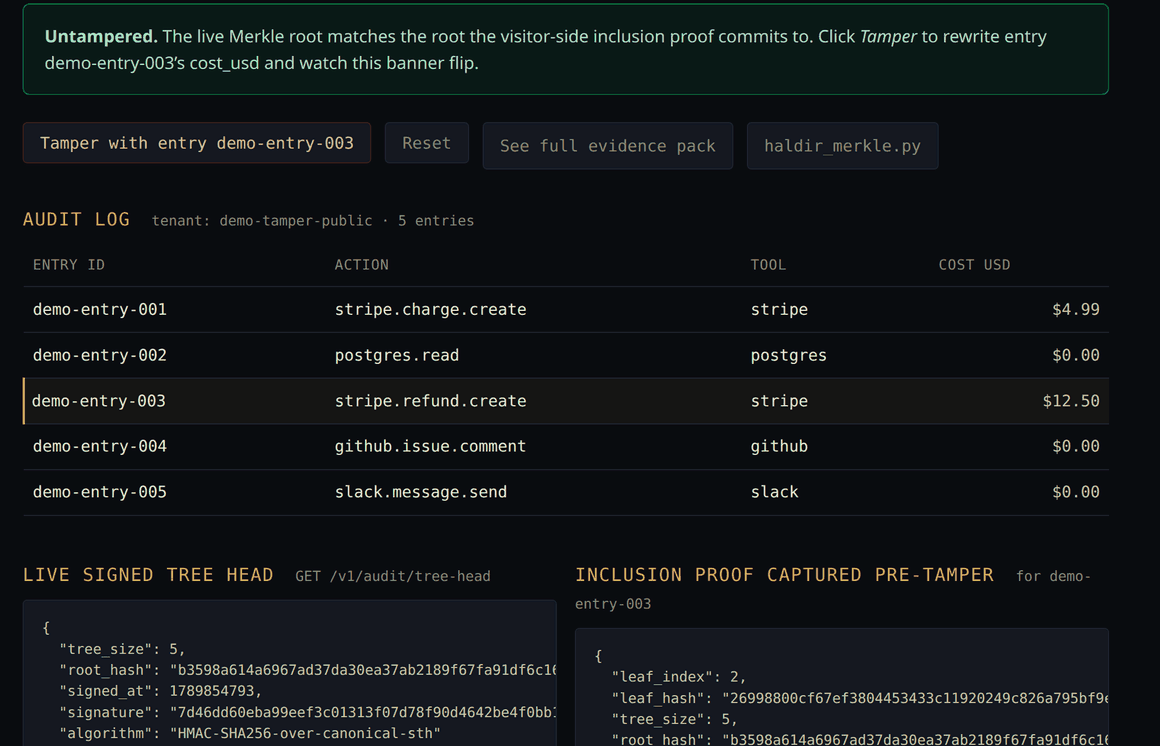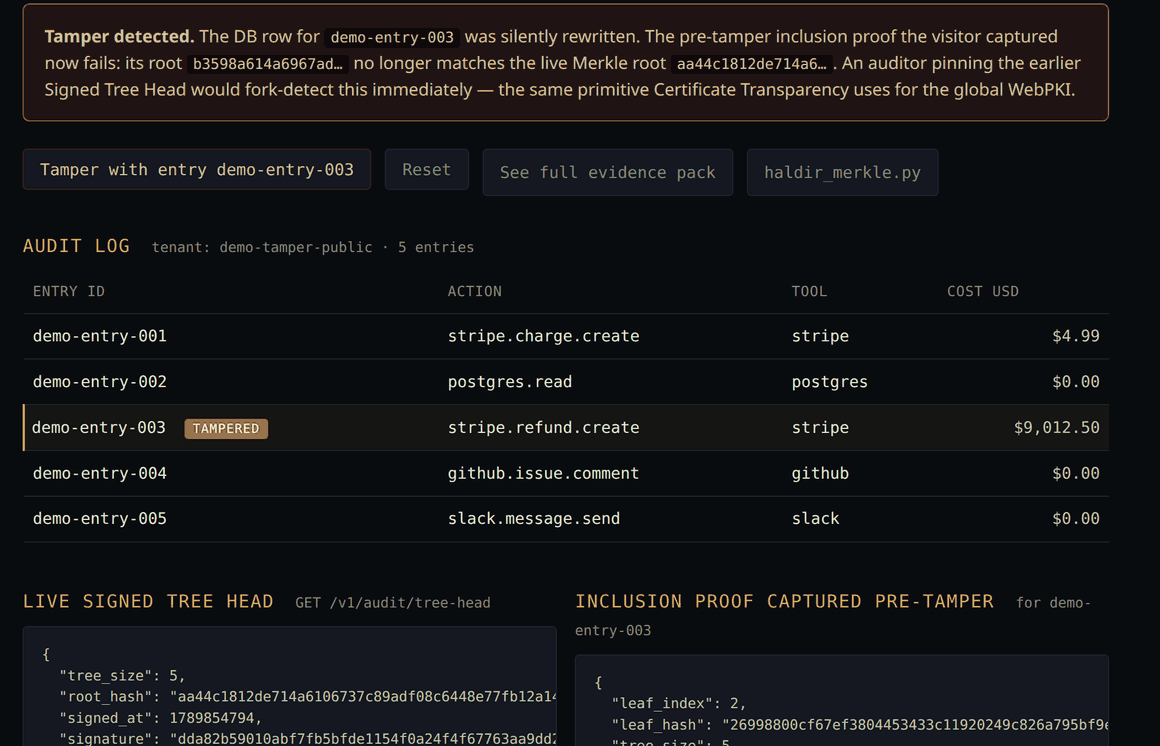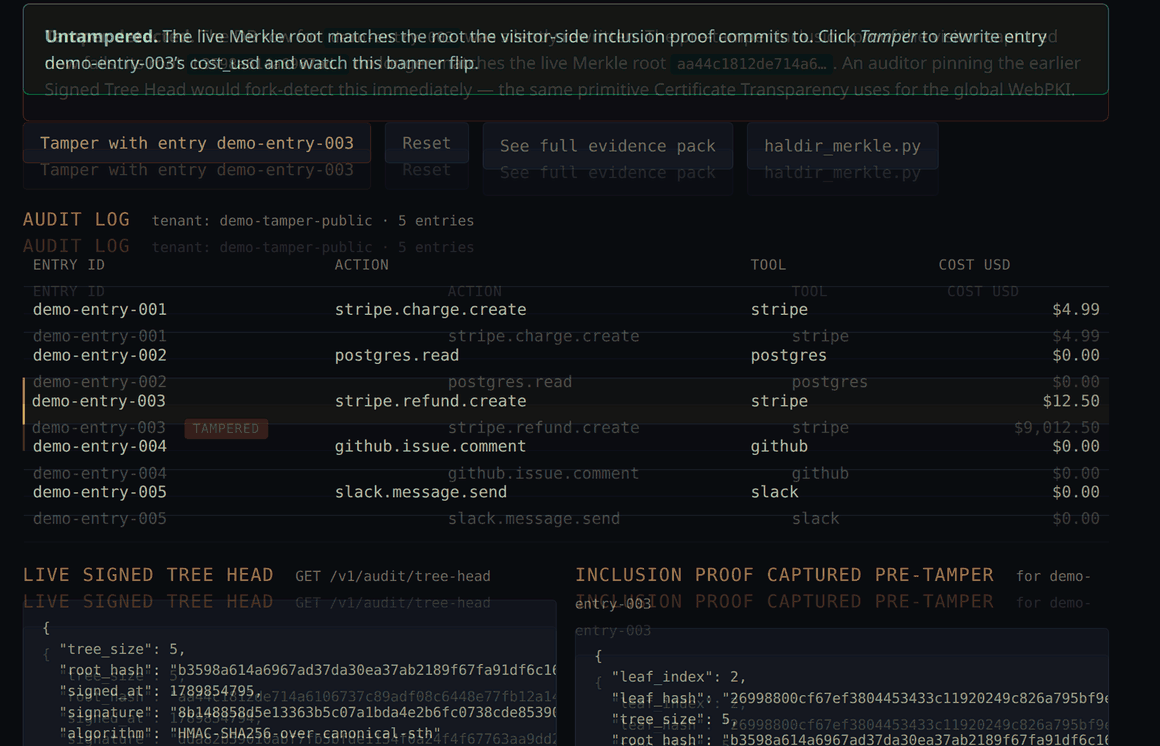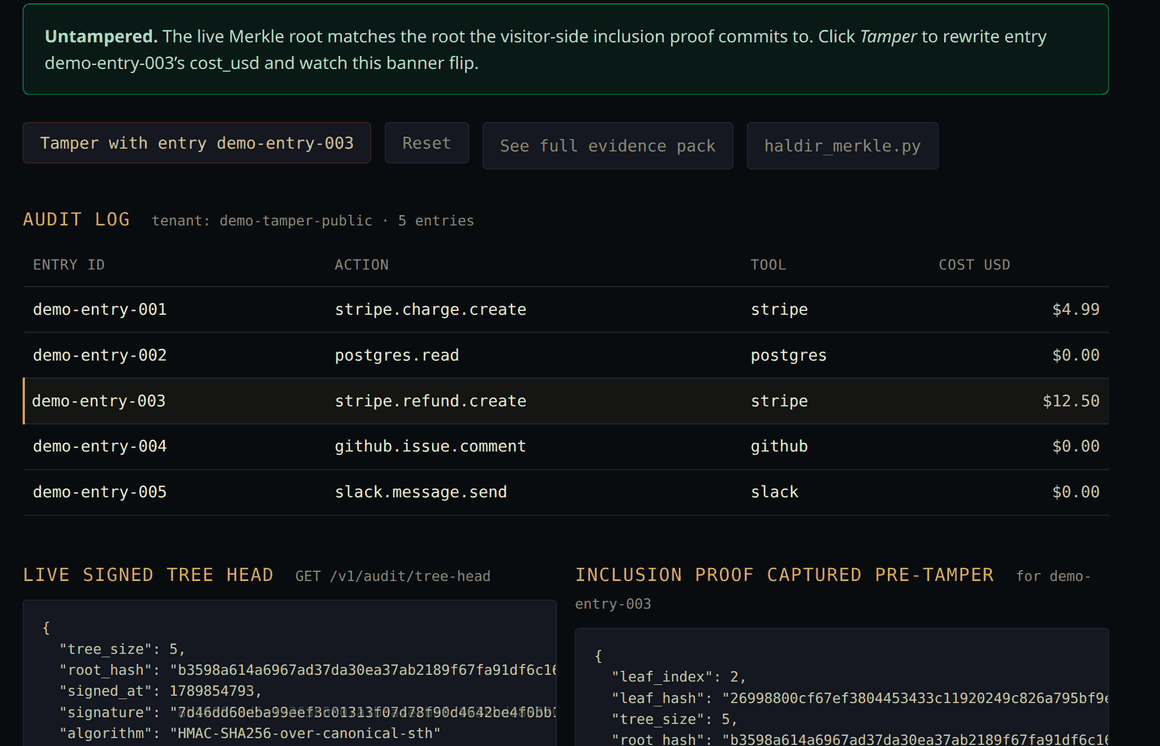
That loop is the whole idea, running live. Someone rewrites a row in the audit log — silently, straight in the database. The entry's inclusion proof no longer matches the live Merkle root, and the verdict flips. Not caught by monitoring, not caught by a diff: caught by arithmetic, because the root is a hash of what the log actually contains and the earlier Signed Tree Head is already pinned somewhere you don't control.
→ Try it yourself. Run haldir serve (below) and open http://127.0.0.1:8000/demo — the same tamper demo, against an instance on your own machine. It ships inside the package, so there is nothing to download and no account involved.
What you get
- Scoped sessions — permissions and spend caps per agent, revocable the moment something looks wrong.
- Encrypted vault — AES-256-GCM. Your agent asks for a secret; the model never sees it. Every ciphertext records which key made it, so you can rotate the encryption key without re-entering a single secret — and without downtime.
- Tamper-evident audit — every call logged into an RFC 6962 Merkle tree with signed tree heads, so history can be proven, not just trusted.
- Human approvals — pause a run on a spend threshold and get a webhook.
That starts a real Haldir on this machine — SQLite, no Docker, no Postgres, no account. It generates an encryption key, applies the schema, mints an API key, and points the CLI at itself, so the next command just works:
From there, point anything at it — the CLI, the Python SDK, an MCP client — or read the API reference at /docs on the instance you started. When you want Postgres and containers, haldir init && haldir dev scaffolds and runs that instead; SELF_HOSTING.md covers the rest.
Works with Claude Code, Cursor, LangChain, CrewAI, AutoGen, LlamaIndex and the Vercel AI SDK — anything that can make an HTTP call or speak MCP. MIT licensed: self-host it, or point at haldir.xyz (free tier, no signup).
See it in action
Here's what Haldir actually looks like — no diagrams, no spec sheets, just screenshots of the real thing.
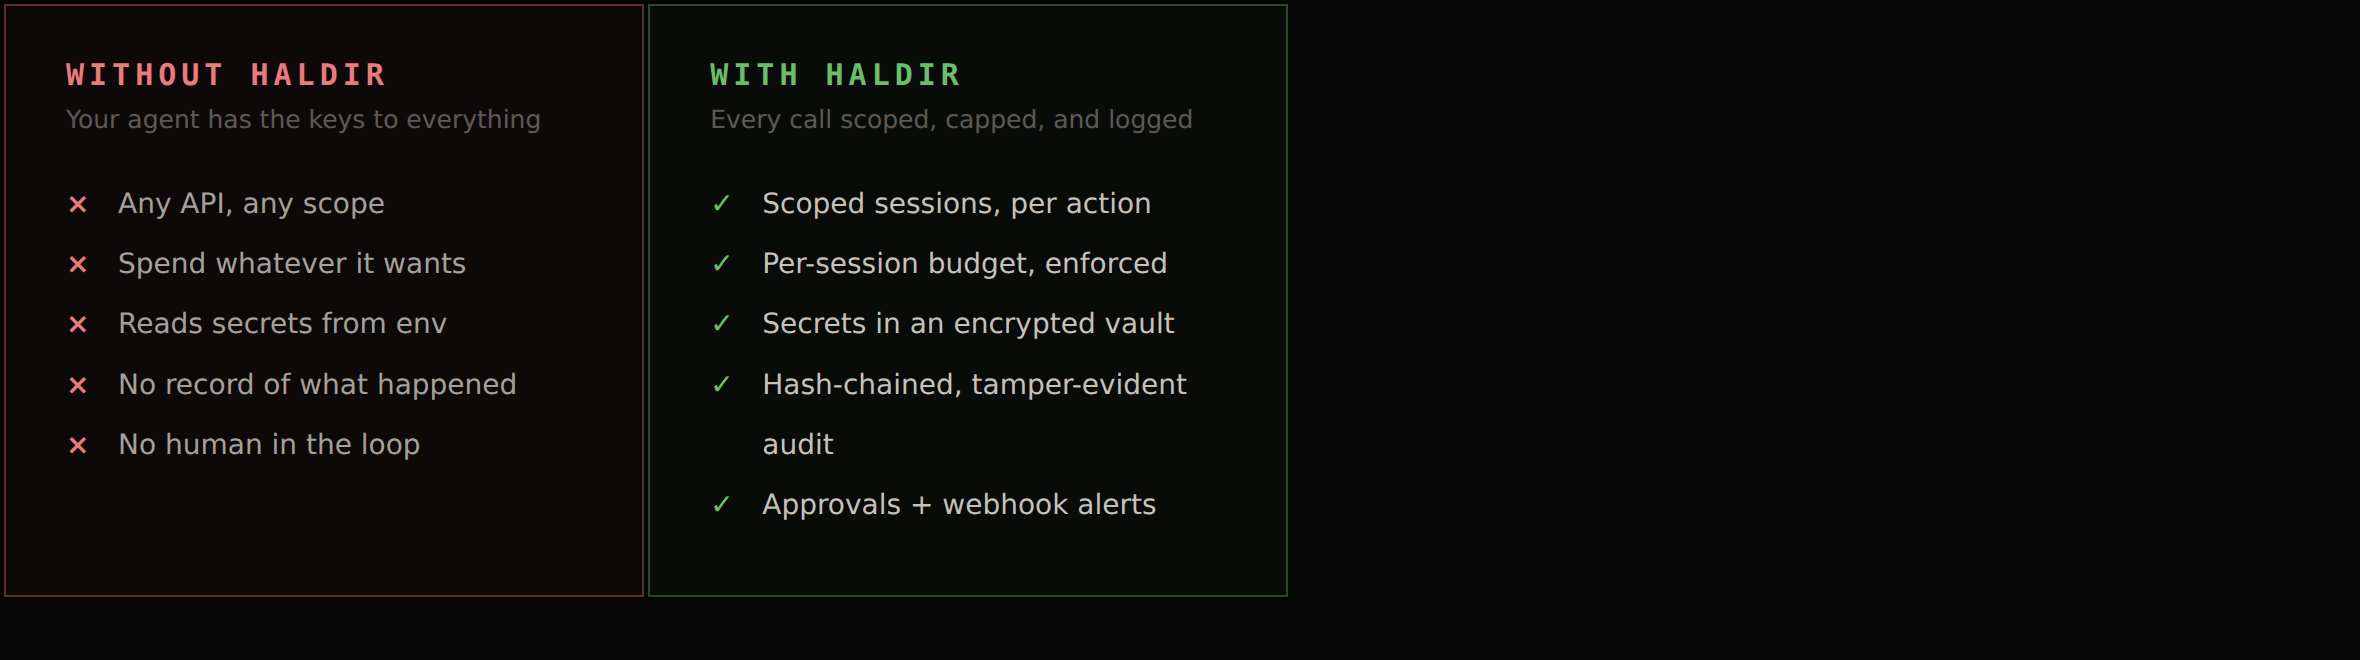
Without Haldir, an agent calls whatever API it wants, spends whatever it wants, and accesses whatever secret it finds — with zero oversight and zero audit trail. With Haldir, every action is scoped, spend-limited, logged immutably, and secrets never leave the vault.
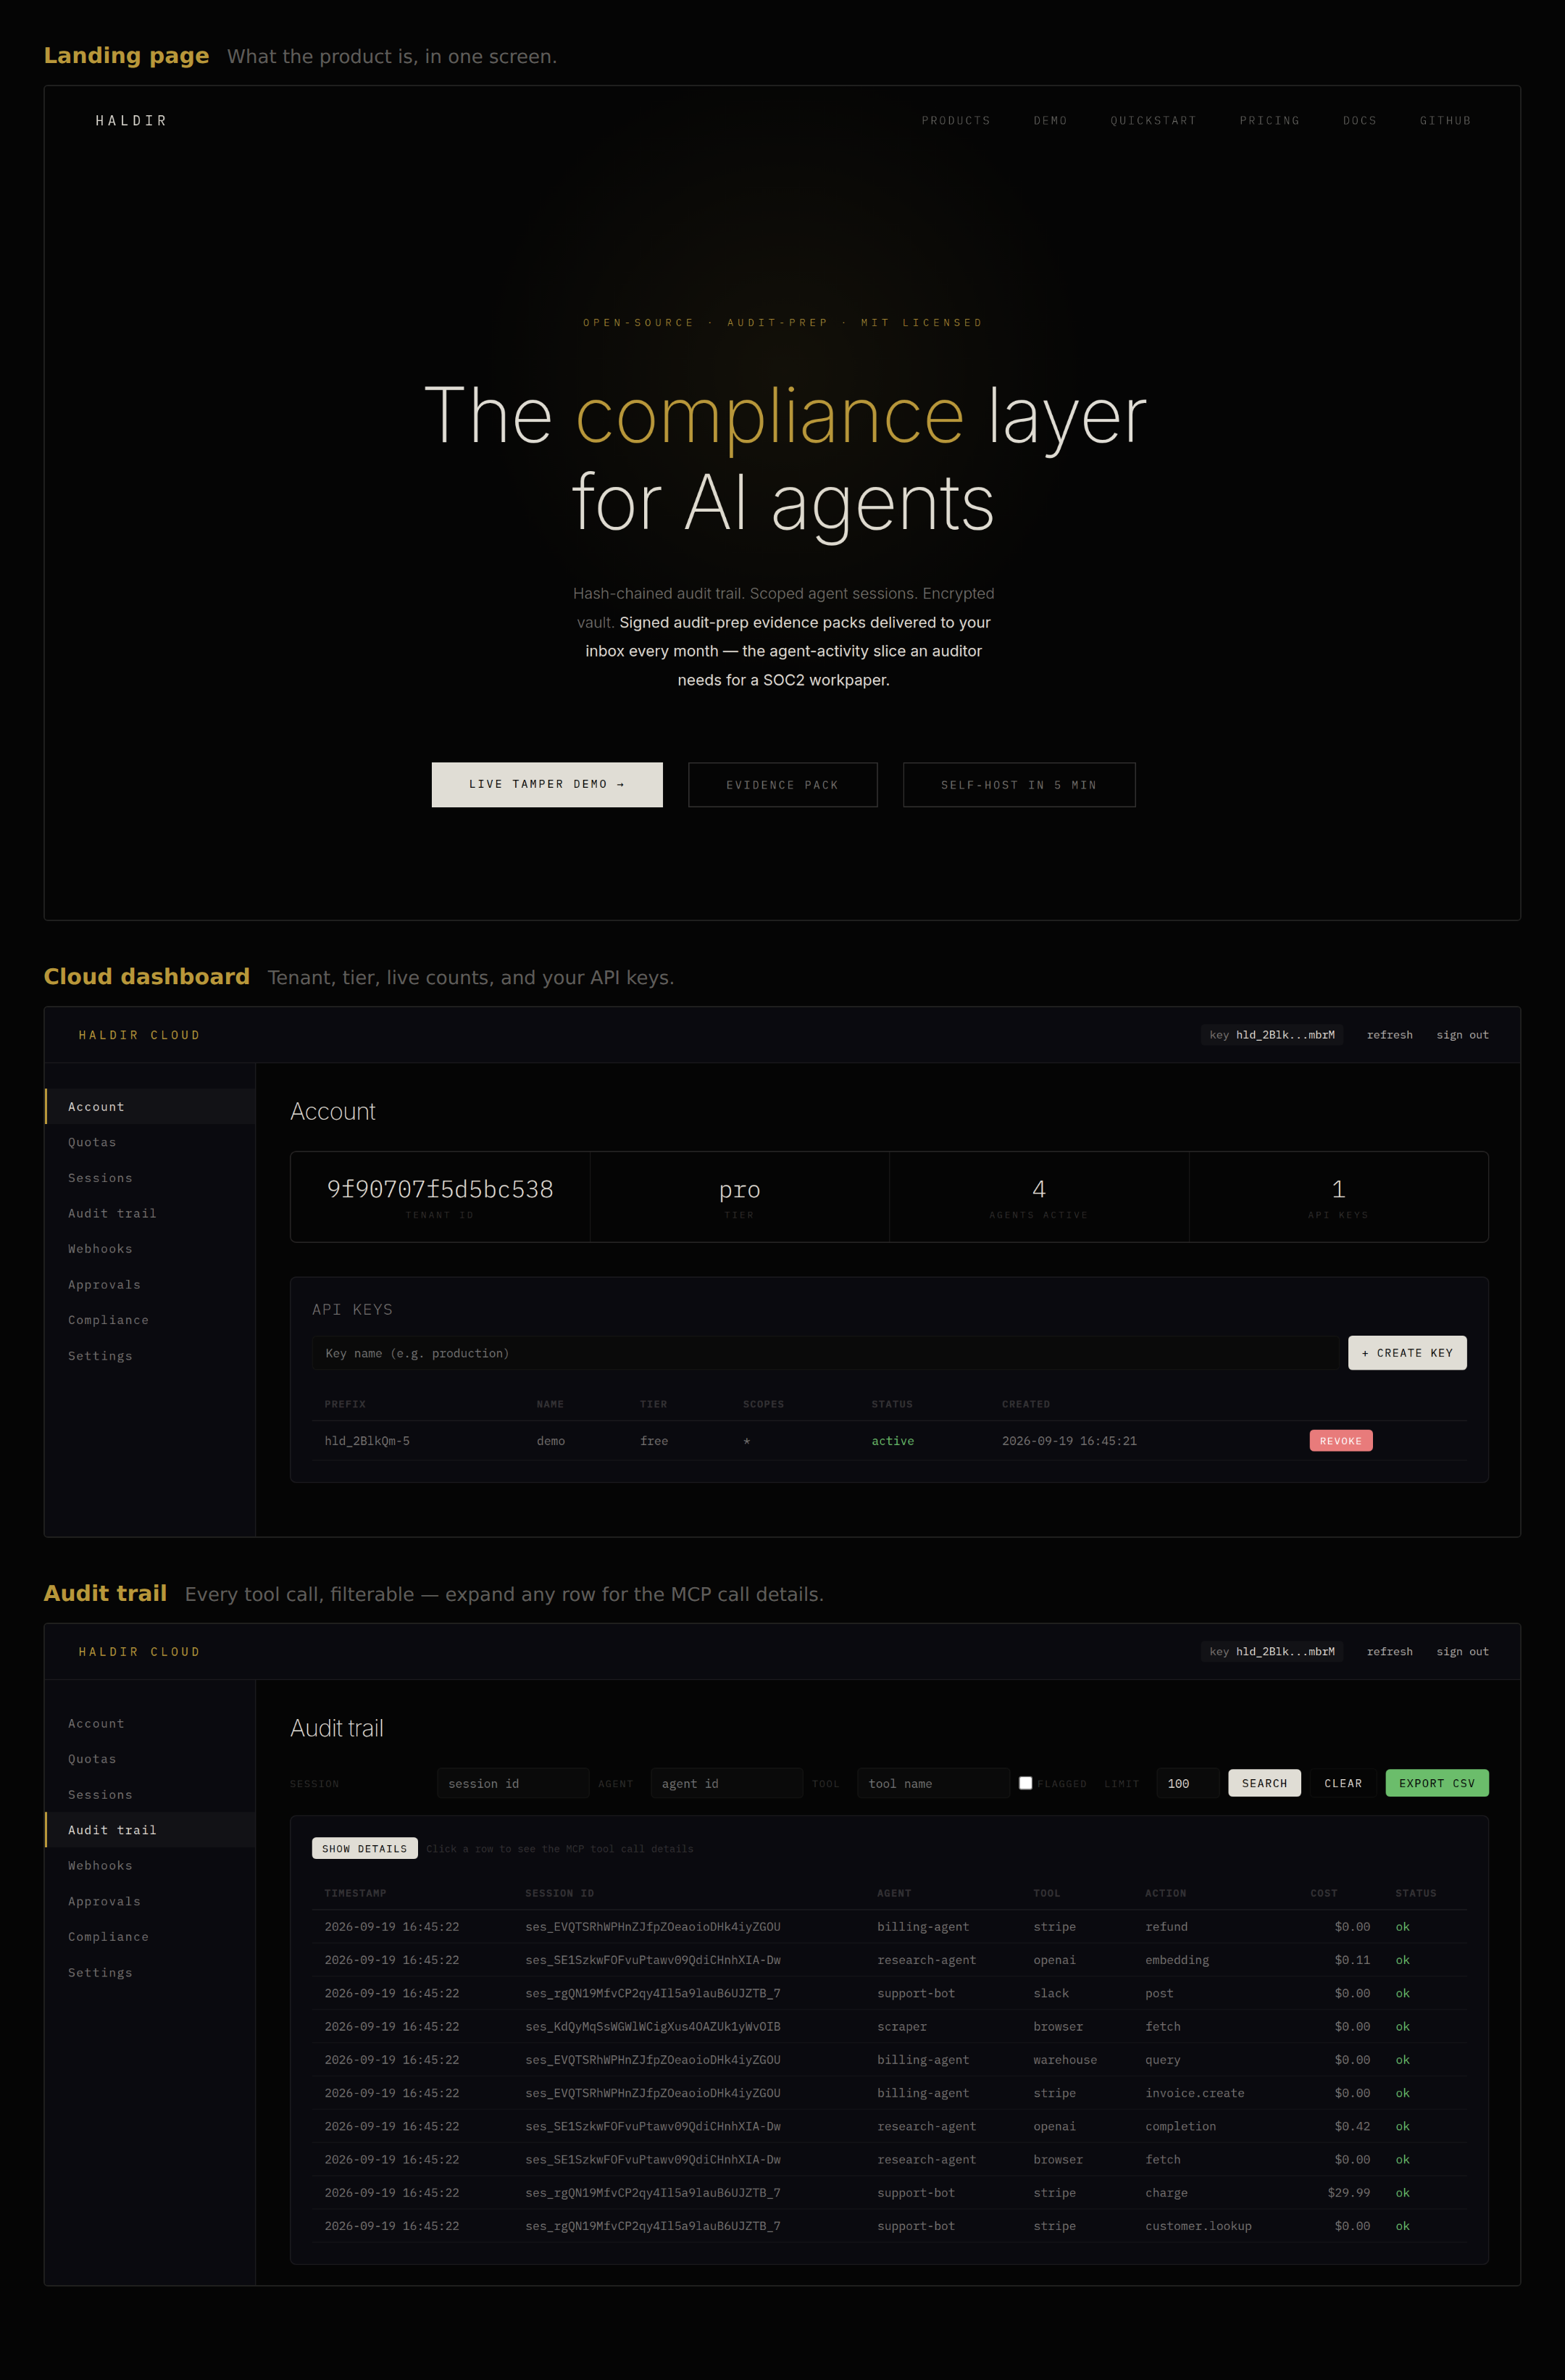
Here's the three things you'd see as a new visitor, in order:
-
Landing page — dark mode, live terminal animation at the top, four product cards (Gate, Vault, Watch, Proxy), a self-host vs cloud comparison, and a call to claim a design partner spot. One page, everything a first-time visitor needs.
-
Cloud dashboard — this is what you see after signing in. A sidebar on the left takes you to any page — account, quotas, sessions, audit, webhooks, approvals, compliance, or settings. The account view shows your tenant, tier, live counts, and API keys by prefix (the full key is never shown again after it's minted, and revoking one never involves a database shell).
-
Audit trail — the killer feature. Filter by session, agent, or tool. Click any row to see the full MCP call details: what tool was called, what upstream API it hit, how long it took, what arguments it sent, and what it returned. This is the one thing that makes the whole product click — you can see exactly what every agent did, when, and with what.
Here's the dashboard with the important parts labeled:
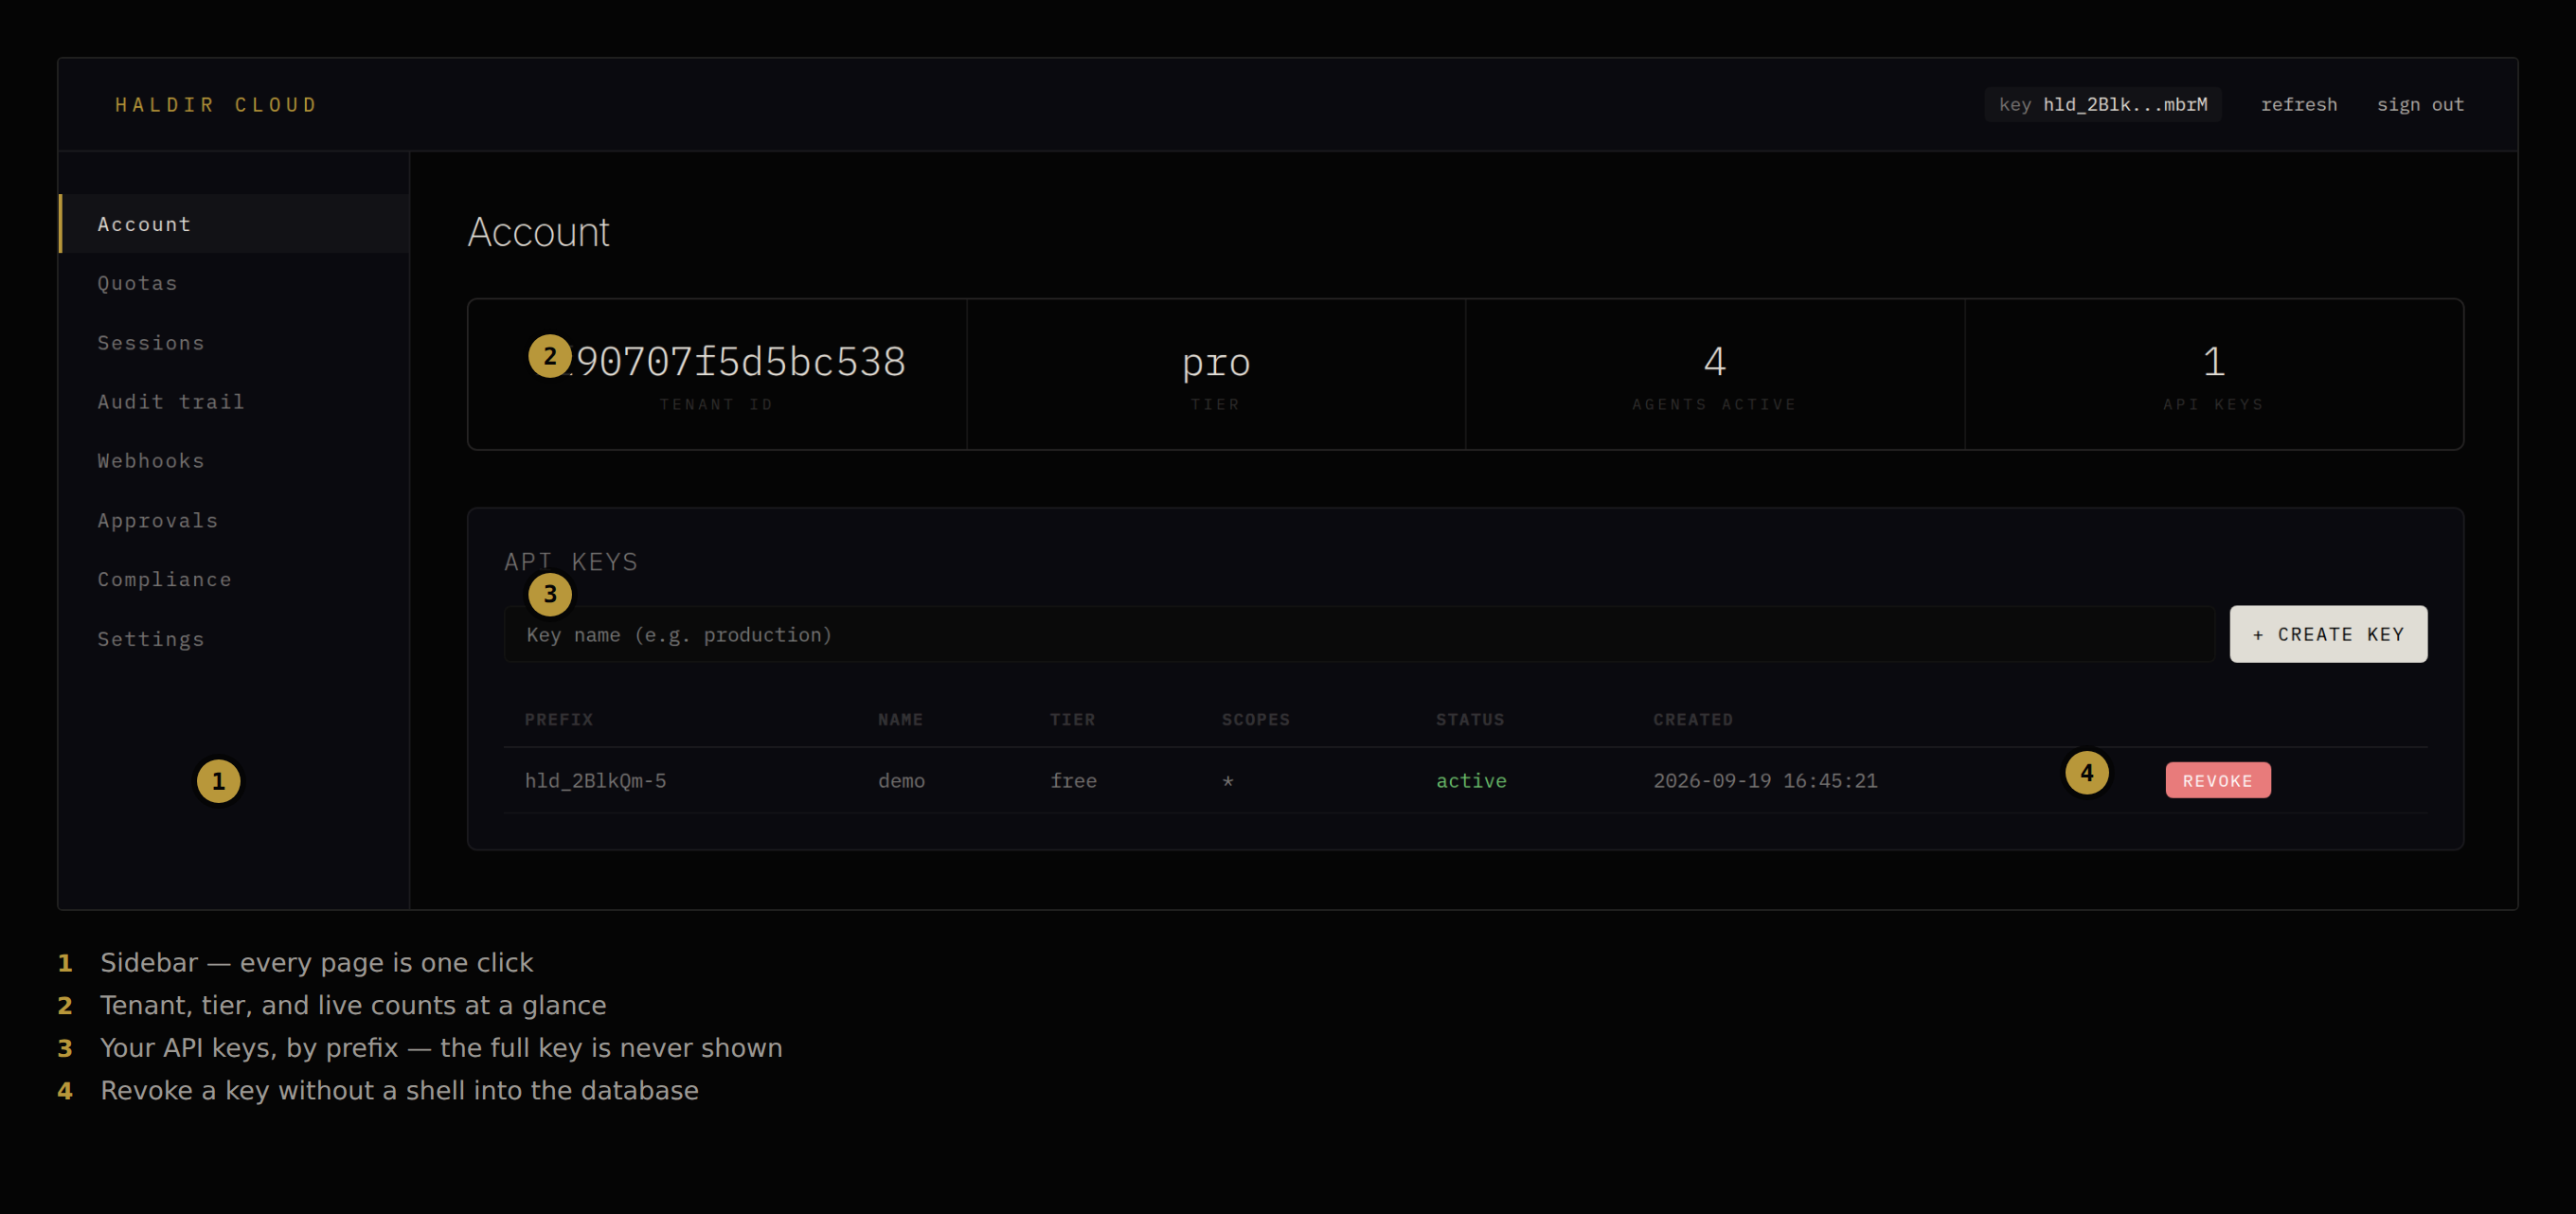
The sidebar on the left takes you anywhere. The numbered markers point at the parts you'll actually use: your tenant and tier, the live counts, and your API keys by prefix — with the revoke button right there, so ending an agent's access never means opening a database shell.
Play with it yourself
All of these ship inside the package and are served by haldir serve, so they work on your machine with no account and nothing to deploy:
→ The tamper demo at /demo/tamper — the one in the GIF above. Rewrite a real log row and watch the inclusion proof stop matching the Merkle root. Nothing is simulated; it is the same Merkle code the API ships.
→ The playground at /demo — four steps walk the happy path (mint a key, open a scoped session, check a permission, write to the audit trail), then three try to break it: spend past the cap, revoke the session mid-flight, and act after revocation. Pick a scope that was never granted in step 03 to see a denial as well as an approval.
→ The gallery at /gallery — every screenshot on this page in one place, if you'd rather look than read.
Want something to run without installing anything? There is a one-file demo binary — no Python, no clone — and a three-probe fixture that ships with the package. Both are in DEMO.md: what to run, what you'll see, and what each probe is built to catch.
The rest of the API
The full reference is at /docs and /openapi.json on whichever instance you are running. Below: the Python quickstart, performance numbers, and compliance mapping.
There is a hosted option at haldir.xyz — free tier, no signup. haldir serve is the path that works today, and the one to reach for if the cloud is not what you want anyway.
Two ways to run
Same product either way.
| Self-host | Cloud (haldir.xyz) | |
|---|---|---|
| Price | Free forever | Free tier + paid plans |
| You run | API + Postgres | Nothing |
| Best for | Regulated, air-gapped, "must own data" | "Just make it work" |
The cloud tier is free to start and needs no signup. We're taking 5 design partners — 30 days, full access, direct line to the founder: sterling@haldir.xyz.
Self-host in 5 minutes
Full self-hosting guide: SELF_HOSTING.md
Cloud (no setup)
That's it — point at https://haldir.xyz, no signup for the free tier.
CLI
Install once, drive the whole platform from the terminal:
haldir --help lists every command and CLI.md is the full
reference — what each one does, the flags it takes, and which commands support
--json (not all of them do; the reference says which).
Why Haldir
AI agents are calling APIs, spending money, and accessing credentials with zero oversight. Haldir is the missing layer:
| Without Haldir | With Haldir |
|---|---|
| Agent has unlimited access | Scoped sessions with permissions |
| Secrets in plaintext env vars | AES-256-GCM encrypted vault |
| No spend limits | Per-session budget enforcement |
| No record of what happened | Immutable, tamper-evident audit |
| No human oversight | Approval workflows with webhooks |
| Agent talks to tools directly | Proxy intercepts + enforces |
Everything on the right is one process in front of your tools. Your agent keeps its existing tool calls; Haldir answers first:

Quick Start (Python)
Under the hood that's four HTTP calls — mint a key, open a session, check a permission, write to the audit chain:

Products
Gate — Agent Identity & Auth
Scoped sessions with permissions, spend limits, and TTL. No session = no access.
Vault — Encrypted Secrets & Payments
AES-encrypted storage. Agents request access; Vault checks session scope. Payment authorization with per-session budgets.
Watch — Audit Trail & Compliance
Immutable log for every action. Anomaly detection. Cost tracking. Compliance exports.
Proxy — Enforcement Layer
Sits between agents and MCP servers. Every tool call is intercepted, authorized, and logged. Supports policy enforcement: allow lists, deny lists, spend limits, rate limits, time windows.
Approvals — Human-in-the-Loop
Pause agent execution for human review. Webhook notifications. Approve or deny from dashboard or API.
MCP Server
Haldir is available as an MCP server with 19 tools for Claude, Cursor, Windsurf, and any MCP-compatible AI:
MCP Tools (the process above registers all 19):
| Governance | Tamper-evidence | Approvals & compliance |
|---|---|---|
haldir_create_session | haldir_verify_audit_chain | haldir_request_approval |
haldir_get_session | haldir_get_tree_head | haldir_get_approval_status |
haldir_check_permission | haldir_get_inclusion_proof | haldir_compliance_score |
haldir_revoke_session | haldir_get_consistency_proof | haldir_build_evidence_pack |
haldir_store_secret | haldir_log_audit_action | haldir_authorize_payment |
haldir_get_secret | haldir_query_audit_trail | |
haldir_list_secrets | haldir_get_spend |
There is one tool catalog. The stdio server (haldir-mcp, or haldir mcp serve) registers all 19; the hosted POST /mcp endpoint implements a 10-tool subset under the same names. A name means the same thing on both surfaces, so a client written against one works against the other.
MCP HTTP Endpoint: POST https://haldir.xyz/mcp
Performance
Haldir is fast enough to sit in the hot path of every agent tool call without becoming the bottleneck.
Single-box HTTP throughput (gunicorn 4 workers, 32 concurrent clients, tuned SQLite backend, every request goes through the full middleware stack — auth, validation, idempotency, metrics, structured logging):
| Endpoint | RPS | p50 | p95 | p99 |
|---|---|---|---|---|
GET /healthz | 1,638 | 19.1 ms | 32.5 ms | 41.6 ms |
GET /v1/status | 1,382 | 22.2 ms | 30.8 ms | 45.4 ms |
GET /v1/sessions/:id | 903 | 29.2 ms | 95.5 ms | 172.1 ms |
POST /v1/sessions (create) | 1,142 | 27.7 ms | 35.2 ms | 39.9 ms |
POST /v1/audit (hash-chain) | 1,092 | 28.7 ms | 37.6 ms | 52.6 ms |
Hardware: 12th-gen Intel Core i3-1215U (8 cores, 8 GB RAM). SQLite is configured with WAL + synchronous=NORMAL + 256 MiB mmap + in-memory temp store — the session-lookup p99 dropped by 52 % versus the untuned path. Postgres deployments (configurable pool via HALDIR_PG_POOL_MIN/MAX) flatten the p99 further still; enable via DATABASE_URL=postgresql://....
Primitive cost (pure-Python, no I/O):
| Primitive | p50 | Notes |
|---|---|---|
Vault.store_secret (AES-256-GCM encrypt + AAD) | < 10 µs | in-memory, no DB write |
Vault.get_secret (AES-256-GCM decrypt + AAD) | < 10 µs | in-memory |
AuditEntry.compute_hash (SHA-256 over payload) | < 10 µs | |
Gate.check_permission over REST | ~50-120 ms | network + DB round-trip, Cloudflare-fronted |
Watch.log_action over REST | ~50-150 ms | includes chain lookup + DB write |
| Full governed-tool envelope (check + log) | ~100-250 ms |
Agents typically wait 500-3000 ms for an LLM completion and 100-1000 ms for an upstream API call, so Haldir's overhead sits inside the noise. Reproduce locally:
Compliance
One endpoint produces an auditor-ready proof-of-control pack covering eight sections, each anchored to a SOC2 trust services criterion:
| # | Section | SOC2 |
|---|---|---|
| 1 | Identity (tenant, subscription, period) | — |
| 2 | Access control (API keys + per-key scopes) | CC6.1 |
| 3 | Encryption (AES-256-GCM, AAD binding) | CC6.7 |
| 4 | Audit trail (entry count, hash chain) | CC7.2 |
| 5 | Spend governance (per-session caps) | CC5.2 |
| 6 | Human approvals (request/decision lifecycle) | CC8.1 |
| 7 | Outbound alerting (webhook delivery rate) | CC7.3 |
| 8 | Document signature (SHA-256 self-hash) | — |
The pack signs itself: a SHA-256 over the canonical JSON of sections 1-7. An auditor receiving an archived pack can re-call /v1/compliance/evidence/manifest and confirm the digest matches — proof the document was not modified after issuance.
JSON for evidence-locker upload, Markdown for the "show this to the auditor" moment, both from the same /v1/compliance/evidence endpoint.
Retention and deletion
Audit data is kept forever by default. When a policy requires otherwise, you can set a window and prune to it — and the prune stays provable:
The audit log is a hash chain, so deleting old entries naively leaves the surviving chain pointing at a hash that no longer exists — which would turn a working audit trail into one that fails verification. Instead, a Signed Tree Head is taken over the log before anything is removed, and the hash of the last deleted entry is recorded as the link across the boundary.
The result is that pruning is not silent. haldir audit verify still passes, and reports what was removed along with the signed Merkle root that commits to it — so the honest answer to an auditor is "entries before this point were deleted under a retention policy, and here is the root they produced at the time." If that commitment cannot be produced, nothing is deleted.
API Reference
Full docs at haldir.xyz/docs — the complete OpenAPI 3.1 spec is at haldir.xyz/openapi.json.
Key endpoints (see the spec for the full surface):
| Endpoint | Method | Description |
|---|---|---|
/v1/keys | POST | Create API key |
/v1/sessions | POST | Create agent session |
/v1/sessions/:id | GET/DEL | Get / revoke session |
/v1/sessions/:id/check | POST | Check permission |
/v1/secrets | POST/GET/DEL | Store / list / delete secrets |
/v1/payments/authorize | POST | Authorize payment |
/v1/audit | POST/GET | Log / query actions |
/v1/audit/spend | GET | Spend summary |
/v1/audit/retention | GET/PUT | Read / set the retention window |
/v1/audit/retention/prune | POST | Prune to the window (needs confirm) |
/v1/audit/retention/checkpoints | GET | Prune history + signed commitments |
/v1/approvals/rules | POST | Add approval rule |
/v1/approvals/request | POST | Request approval |
/v1/approvals/:id/approve | POST | Approve |
/v1/approvals/:id/deny | POST | Deny |
/v1/webhooks | POST/GET | Register / list webhooks |
/v1/proxy/upstreams | POST | Register upstream MCP server |
/v1/proxy/call | POST | Call through the proxy |
/v1/usage | GET | Usage stats |
/v1/metrics | GET | Platform metrics |
Agent Discovery
Haldir is discoverable through every major protocol:
| URL | Protocol |
|---|---|
haldir.xyz/openapi.json | OpenAPI 3.1 |
haldir.xyz/llms.txt | LLM-readable docs |
haldir.xyz/.well-known/ai-plugin.json | ChatGPT plugins |
haldir.xyz/.well-known/mcp/server-card.json | MCP discovery |
haldir.xyz/mcp | MCP JSON-RPC |
smithery.ai/server/haldir/haldir | Smithery registry |
pypi.org/project/haldir | PyPI |
Design partners wanted
Live now: haldir.xyz · API Docs · OpenAPI Spec · Smithery
We're taking 5 design partners — 30 days free, full access, direct line to the founder. If you're shipping AI agents to production, email sterling@haldir.xyz.
License
MIT
Links
- Website: haldir.xyz
- API Docs: haldir.xyz/docs
- Smithery: View on Smithery
- PyPI: haldir
- OpenAPI: haldir.xyz/openapi.json