This listing appears offline
Our automated checks couldn’t reach the source repository, so we’ve removed it from search, browse, and the API — this page stays reachable at this direct link only. If this is your project, claim it to fix the link and restore visibility.
Claim this listingsecurityssdclcompliancedocument-parsinglangchain
AI-powered SSDLC platform automating security document assessment across all software lifecycle phases with multi-format parsing and RAG knowledge ba…
Quick Install
Automated & IDE SetupCopy the AI prompt to install this server into Claude Code, Cursor, or another agent — or use 1-click editor setup below.
One-click editor setup isn’t available for this listing yet — we don’t have a confirmed install command, and we’d rather show nothing than point your editor at the wrong package or host. Follow the project’s own setup instructions, linked above.
Manual Client & Custom JSON ConfigExpand JSON ▾
No confirmed setup config for this listing yet. We only publish a config block when the install details come from the project itself — its README, its docs, or a verified owner. We haven’t found those for arthurpanhku/DocSentinel, and we’d rather show nothing than a guess you’d paste into your client. Follow the project’s own setup instructions for the current steps.
Overview
Use cases
Automate security review of requirements, design, development, testing, deployment, and operations documents
Extract security requirements and identify compliance obligations from project documents
Generate automated threat models and security architecture reviews
Analyze SAST/DAST reports and prioritize vulnerabilities
Integrate security assessments into CI/CD pipelines and multi-agent AI platforms
Key features
Full SSDLC phase coverage with dedicated AI personas
Multi-format document parsing (PDF, Word, Excel, PPT, text)
RAG knowledge base for policy and compliance reference
Support for multiple LLMs including OpenAI, Claude, Qwen, and Ollama
Structured JSON/Markdown output with risks, compliance gaps, and remediation
LangGraph-based stateful agent orchestration with conditional branching
Capabilities & Tool Schemas
Inspect callable tools, capabilities, and parameters exposed to AI agents by DocSentinel.
Extracted Tool Capabilities
Full SSDLC phase coverage with dedicated AI personas
Multi-format document parsing (PDF, Word, Excel, PPT, text)
RAG knowledge base for policy and compliance reference
Support for multiple LLMs including OpenAI, Claude, Qwen, and Ollama
Structured JSON/Markdown output with risks, compliance gaps, and remediation
LangGraph-based stateful agent orchestration with conditional branching
Documentation Overview
Anime cyber kitsune sentinel for the DocSentinel console and documentation.
DocSentinel
AI-powered SSDLC platform — Secure your software from requirements to operations





What is DocSentinel?
DocSentinel is an AI-powered SSDLC (Secure Software Development Lifecycle) platform for security teams. It automates security activities across all six phases of the software development lifecycle using intelligent AI agents orchestrated by LangGraph and powered by LangChain. It automates the review of security-related documents, forms, and reports — from requirements and design through development, testing, deployment, and operations — comparing inputs against your policy and knowledge base to produce structured assessment reports with risks, compliance gaps, and remediation suggestions.
Instead of only reviewing documents at the pre-release stage, DocSentinel embeds security from day one:
| SSDLC Phase | What DocSentinel Does |
|---|---|
| Requirements | Extract security requirements, identify compliance obligations (GDPR, PCI DSS, SOC2) |
| Design | Automated threat modeling (STRIDE/DREAD), security architecture review, SDR reports |
| Development | Secure coding assessment, SAST findings triage, coding guidance |
| Testing | SAST/DAST report analysis, penetration test review, vulnerability prioritization |
| Deployment | Configuration security review, hardening assessment, release sign-off |
| Operations | Vulnerability monitoring, incident response assistance, log audit |
Built as a React console + FastAPI service + MCP/A2A agent gateway, DocSentinel integrates into local security review workflows, CI/CD pipelines, AI agents, and multi-agent platforms without giving external agents approval authority.
- LangGraph orchestration: Stateful, graph-based agent workflows with conditional branching per SSDLC stage.
- Multi-format input: PDF, Word, Excel, PPT, text — parsed into a unified format for the LLM.
- Knowledge base (RAG): Upload policy and compliance documents; the agent uses them as reference when assessing.
- Multiple LLMs: Use OpenAI, Claude, Qwen, or Ollama (local) via a single interface.
- Structured output: JSON/Markdown reports with risk items, compliance gaps, and actionable remediations.
Ideal for enterprises that need to scale security assessments across many projects and SSDLC stages without proportionally scaling headcount.
Product Tour
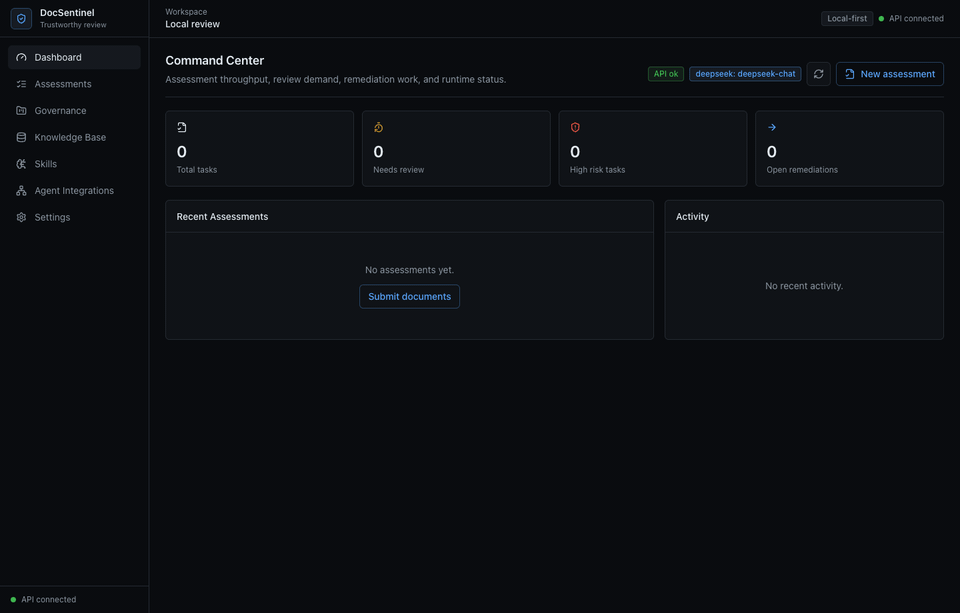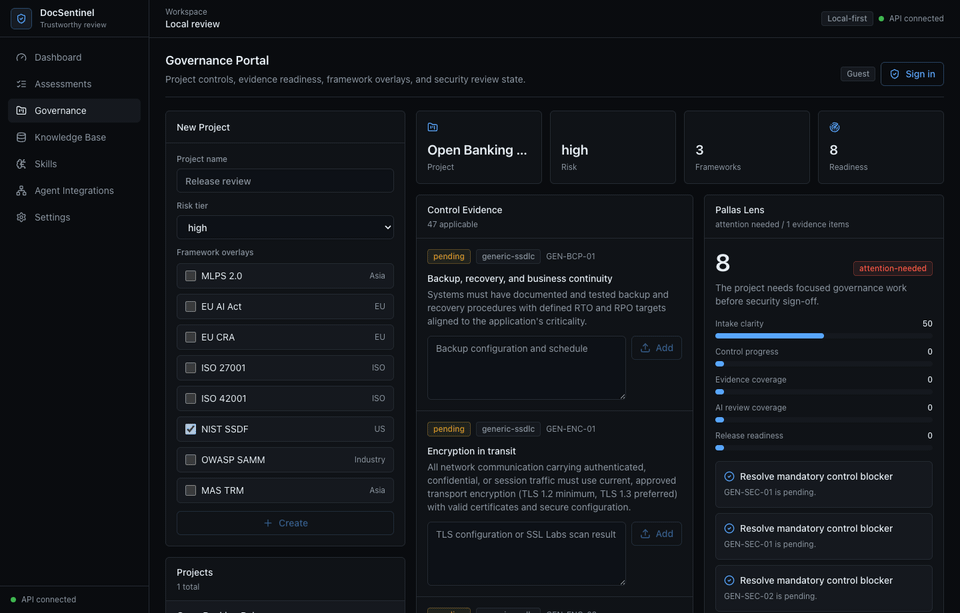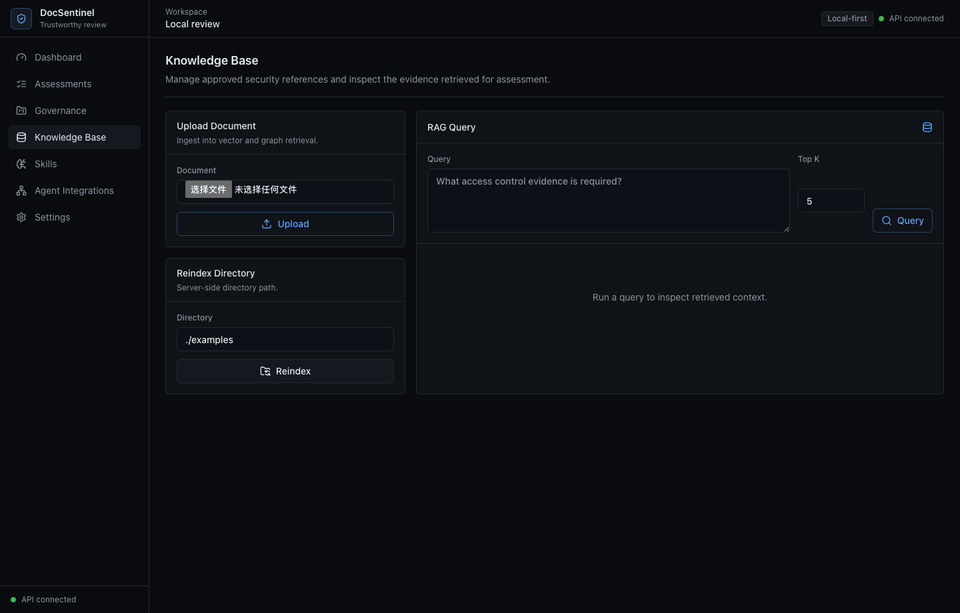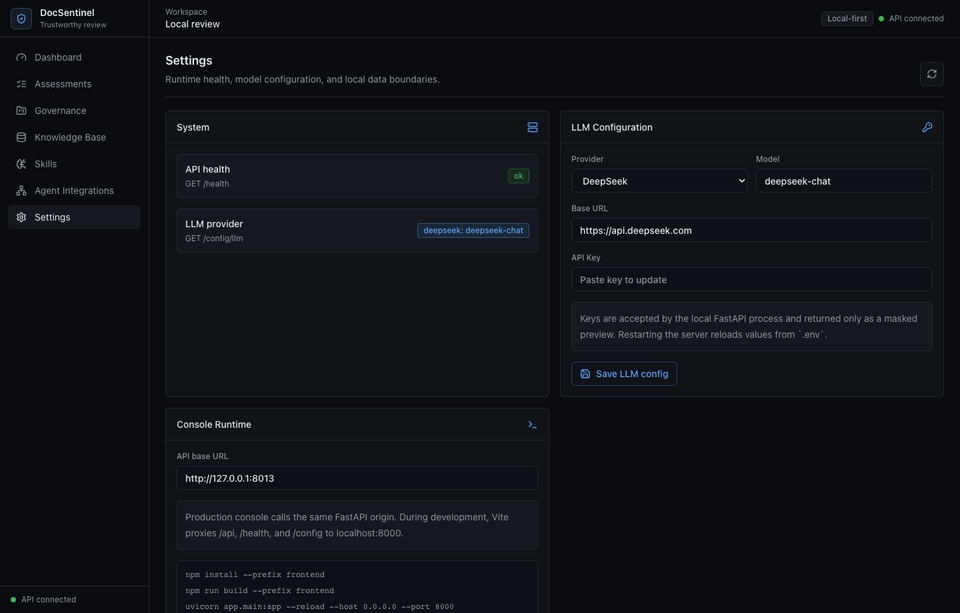
The local React console brings the main workflow into one operational surface:
- Command Center: live API and LLM status, assessment throughput, review demand, remediation queues, and recent activity.
- Assessment Workbench: upload project documents, choose SSDLC phase/skill, inspect AI-generated risks, and complete human review.
- Governance Portal: create projects, apply public framework overlays, generate controls, submit evidence, and track Pallas Lens readiness.
- Knowledge Base: ingest policies and standards for RAG-backed review.
- Agent Integrations: expose governed MCP and A2A tools to coding agents and multi-agent platforms without granting approval authority.
- Settings: switch providers such as DeepSeek, OpenAI, Anthropic, Qwen, or Ollama; API keys are accepted locally and only shown as masked previews.
Why DocSentinel?
| Pain Point | DocSentinel Solution |
|---|---|
| Fragmented SSDLC coverage Most tools only address testing/deployment. | Full lifecycle agents cover all 6 SSDLC phases with dedicated AI personas. |
| Fragmented criteria Policies, standards, and precedents are scattered. | Single knowledge base ensures consistent findings and traceability. |
| No automated threat modeling Threat models are created ad-hoc. | Design Agent generates STRIDE/DREAD threat models from architecture docs. |
| Heavy questionnaire workflow Endless review cycles. | Automated first-pass and gap analysis reduces manual back-and-forth rounds. |
| SAST/DAST report overload Too many findings, too little context. | Testing Agent triages, prioritizes, and maps findings to threat models. |
| Pre-release review pressure Everything lands on security at the end. | Shift-left approach catches issues early in requirements and design. Structured reports help reviewers focus on decision-making. |
| Scale vs. consistency Manual reviews vary by reviewer. | LangGraph workflows and unified pipeline ensure consistent, auditable assessment across projects. |
| SSDLC coverage gaps Security involvement is uneven across lifecycle stages; early stages get less scrutiny. | Stage-aware assessment covers all 6 SSDLC stages with dedicated skills and checklists. |
See the full problem statement and SSDLC phase details in SPEC.md.
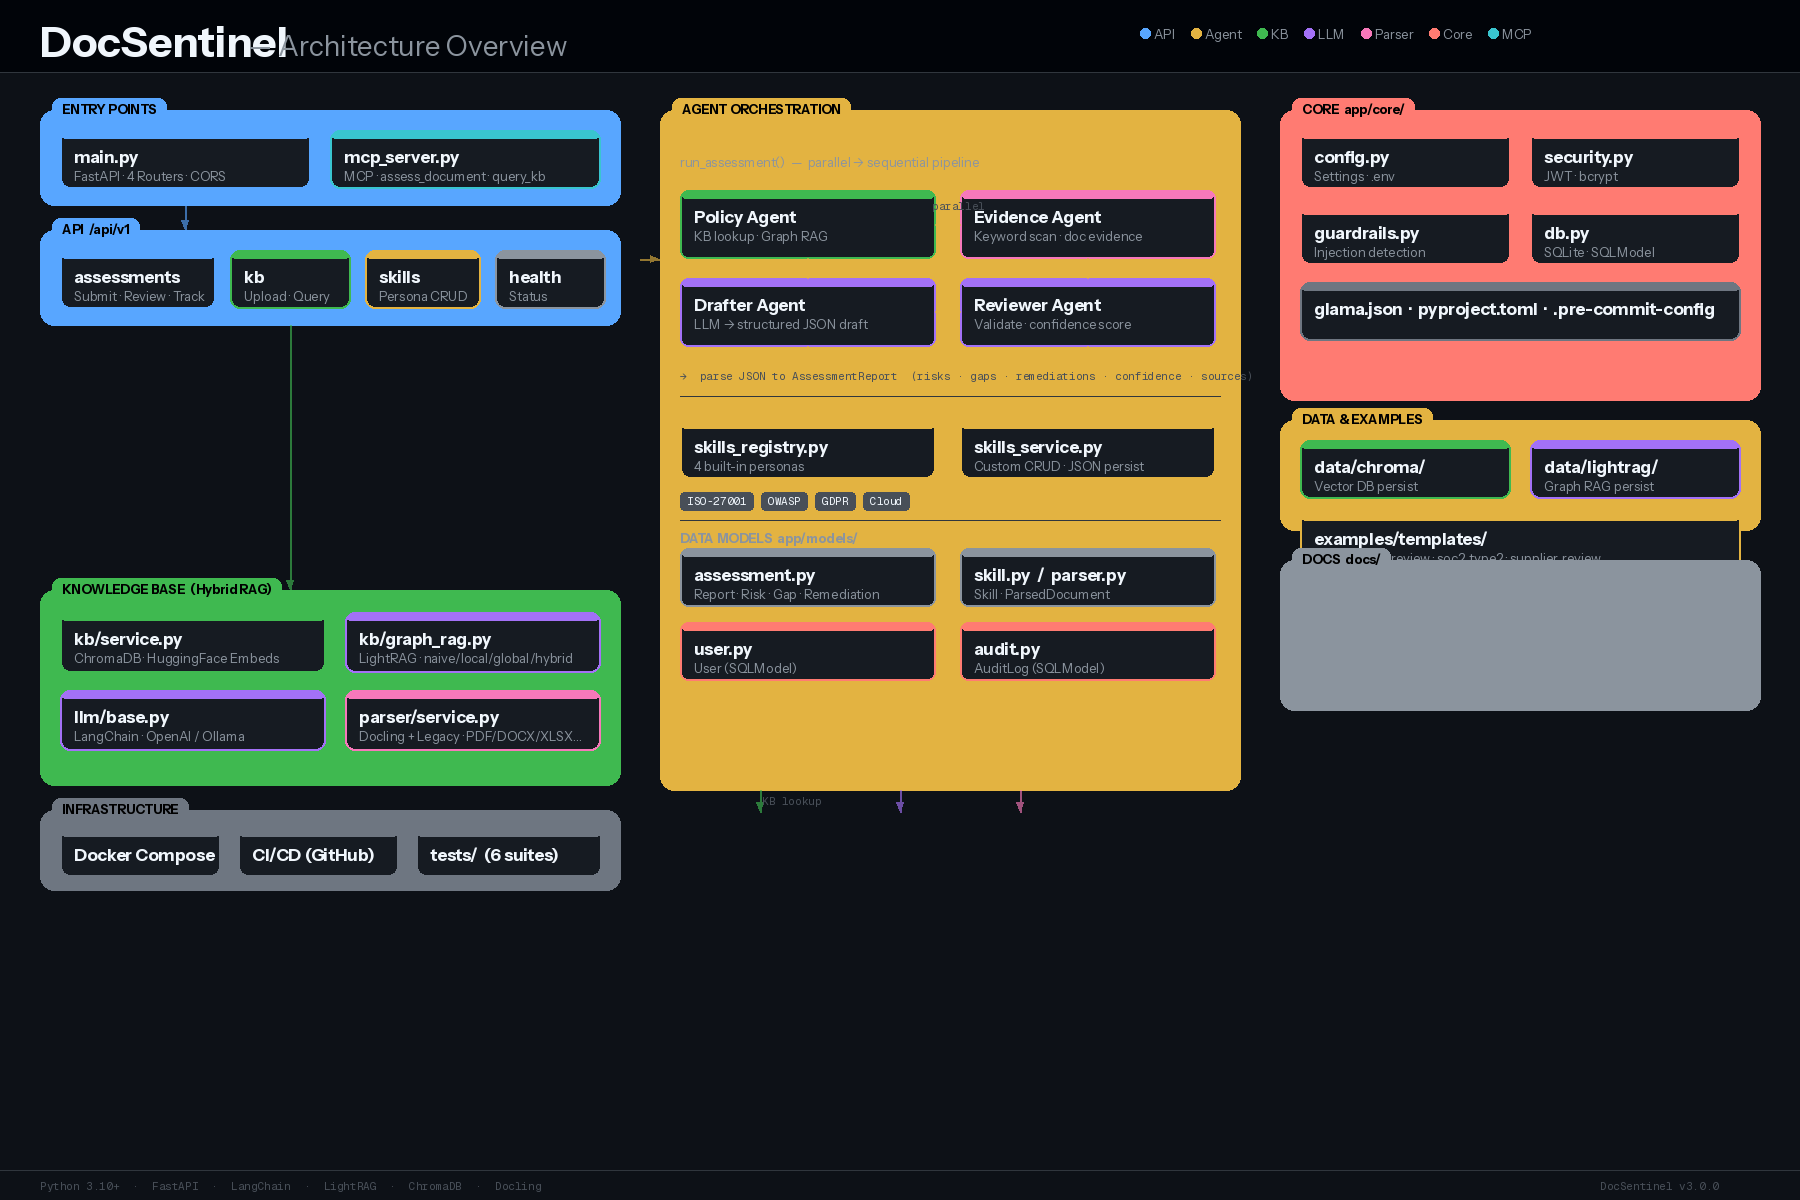
Architecture
DocSentinel is a React Console + FastAPI application with three governed
entry paths: REST APIs for the console and CI, MCP tools for coding agents, and
A2A JSON-RPC for remote agent delegation. These entry paths converge on the
same AssessmentService, LangGraph assessment pipeline, knowledge base, and
human-review lifecycle. Governance workflows from PallasGuard are now a
first-class domain beside assessment, backed by SQLModel records, policy packs,
control evidence, audit trails, and Pallas Lens readiness scoring.
Related MCP Servers

Adoption & maintenance
Factual signals from GitHub, npm, and our automated checks — not a rating.
GitHub stars
90
Stargazers on the source repository.
Last commit
1mo ago
Most recent push to the default branch.
Directory activity
3 views
Config copies, upvotes, and views on AllMCPs.
Reviews
No reviews yet — be the first to share how this listing worked for you.
Frequently Asked Questions about DocSentinel
AllMCPs Directory Badge
Showcase your server listing on GitHub or your project documentation. Embed this dynamic SVG badge to highlight official listing status and live engagement.
Badge Style:
Live Dynamic SVG Preview
Markdown (GitHub README)
[](https://allmcps.com/mcp/arthurpanhku-docsentinel)HTML Embed
<a href="https://allmcps.com/mcp/arthurpanhku-docsentinel"><img src="https://allmcps.com/api/badge/arthurpanhku-docsentinel?style=directory" alt="DocSentinel on AllMCPs" /></a>Technical Specs & Signals
CategorySecurity
PricingBring your own API key (usage-based cost)
47Quality signal: Fair · 47/100How this signal is calculated ▾
Server availabilityNot measured
Not scored for repo-hosted servers — we can't reach the running server, only its GitHub page. Hosted MCP endpoints are health-checked live.
Verified ownership10/20
Documentation & tools19/30
Adoption & activity6/15
Community engagement0/10
A guidance signal from public completeness & health data — not a user rating. New listings start lower and rise as they add docs, get verified, and grow adoption. Signals we can't observe for a listing are skipped, not counted against it.
Own this project?
This directory is pre-filled from public sources. Claim via GitHub README, site badge, or DNS TXT to unlock edit access and the Official badge — proof is checked automatically, then reviewed by our team.
Free dofollow backlink: add your website and place the AllMCPs badge on it — no claim needed. We detect it automatically and keep it verified as long as the badge stays live.
Claim & get free dofollowShare & Embed
Add our SVG badge (dark/light directory styles) or embeddable widget to your site.